Today, I started using my corporate sanctioned AWS account and deployed a Linux jump box. I created a key-pair and then struggled to log in since most of the documentation out there said to use ec2-user . Needless to say, that was not correct. I will use my SecureCRT instance to connect via SSH. I will hopefully help some folks out.
Here we go.
AWS Instance Deployment
Log into your AWS console and create an instance. In my case, I did an Ubuntu Server with minimal resources. I am going to use it for NMAP scans and testing remote connectivity.
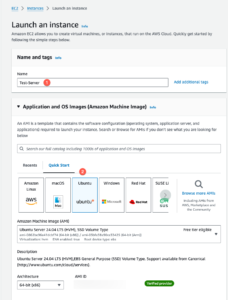
Pick the distro of your choice.
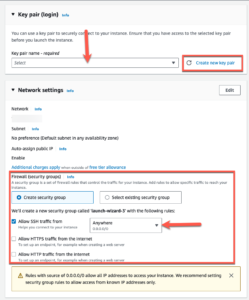
As you can see in the screenshot, we are going to create a new key-pair or use an existing one. Since this is my first device in this environment, I created a new one. Save this file in a safe place.
NOTE: Remember your Security Group Is like your firewall of sorts. You want to limit outside access as much as possible. Later it will be sitting behind a pair of FortiGates in AWS but for now, it only allows my public IP to connect.
SecureCRT configuration
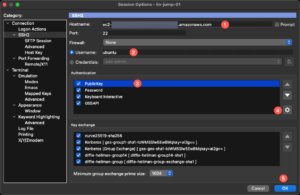
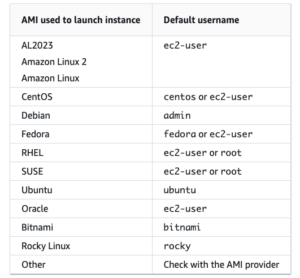
Enter the hostname or IP address of the instance (1). The username (2) is dependent on the distro you installed (See below) . Next you will need to move the Public Key (3)Authentication to the top then point to the file (4)
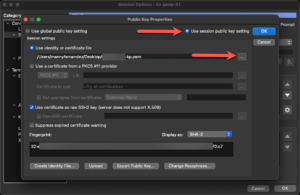
Enter the path to the pem file. and choose either the session or the global. Since I have different key-pairs for different customers and devices, I do for the session.
You can also use the ppk output when you create the key-pair for PuTTY or you can use the pem for SecureCRT and openssh on the CLI.