By Manny Fernandez

January 26, 2026

InfoSec Monkey Lab – Update

InfoSec Monkey Lab – Update

Getting a new server and setting up the new lab.  I will be creating a detailed post and possibly a video showing how I deployed it.  I will be using ProxMox & eve-ng.  The idea is to create a NAC, AD VPNv2, BGP on Loopback SD WAN and a few more.  The WAN emulator is still up in the air, although my buddy is running a nice one I may try.

We are going to have 4 ISP carriers with each FortiGate being multi-homed to at least two of them.  They will pass through the WAN emulator so we can inject jitter, latency and packet-loss on the SD WAN links.  We are also going to have a FortiNAC lab where we have some Windows, Linux, PLCs, and IOT devices.  I will have the Cisco router and ASA to test Security Group Tags (SGT).

We will also have the ability to do FortiClient with Cloud-Based EMS.

More to come.
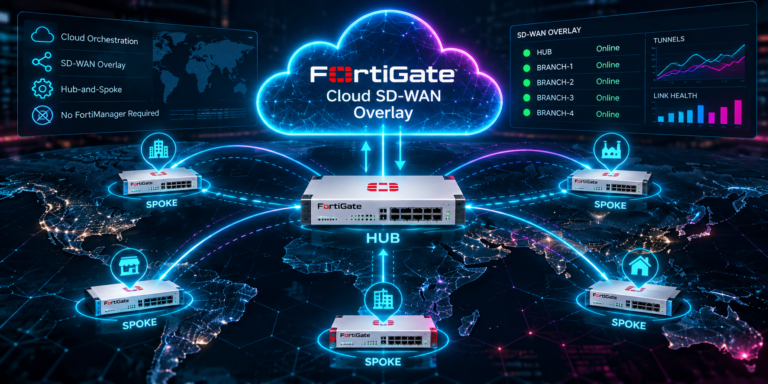
FortiGate Cloud SD-WAN Overlay: Hub-and-Spoke Orchestration Without a FortiManager

FortiGate Cloud SD-WAN Overlay: Hub-and-Spoke Orchestration Without a FortiManager

Configure a FortiGate Cloud SD-WAN overlay with Fortinet-hosted hubs. Deploy ADVPN hub-and-spoke tunnels without FortiManager using this step-by-step guide.

Read More
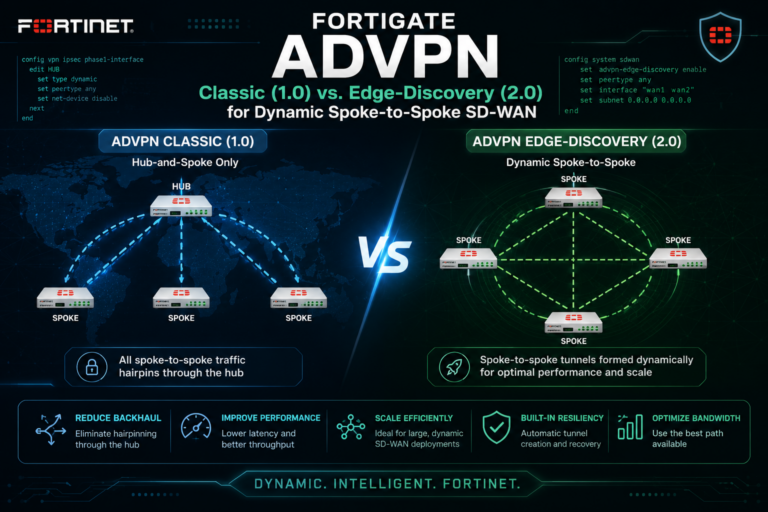
FortiGate ADVPN: Classic (1.0) vs. Edge-Discovery (2.0) for Dynamic Spoke-to-Spoke SD-WAN

FortiGate ADVPN: Classic (1.0) vs. Edge-Discovery (2.0) for Dynamic Spoke-to-Spoke SD-WAN

Compare FortiGate ADVPN 1.0 vs 2.0 for SD-WAN. Deploy dynamic spoke-to-spoke tunnels with exact FortiOS 7.2 and 7.4 configs. No fluff, just working steps.

Read More
VPN Hair-Pinning on Fortigate Firewalls

VPN Hair-Pinning on Fortigate Firewalls

Configure Fortigate VPN hair-pinning to route traffic between spokes via the hub. Learn to adjust Phase II selectors and firewall policies for secure spoke-to-spoke...

Read More