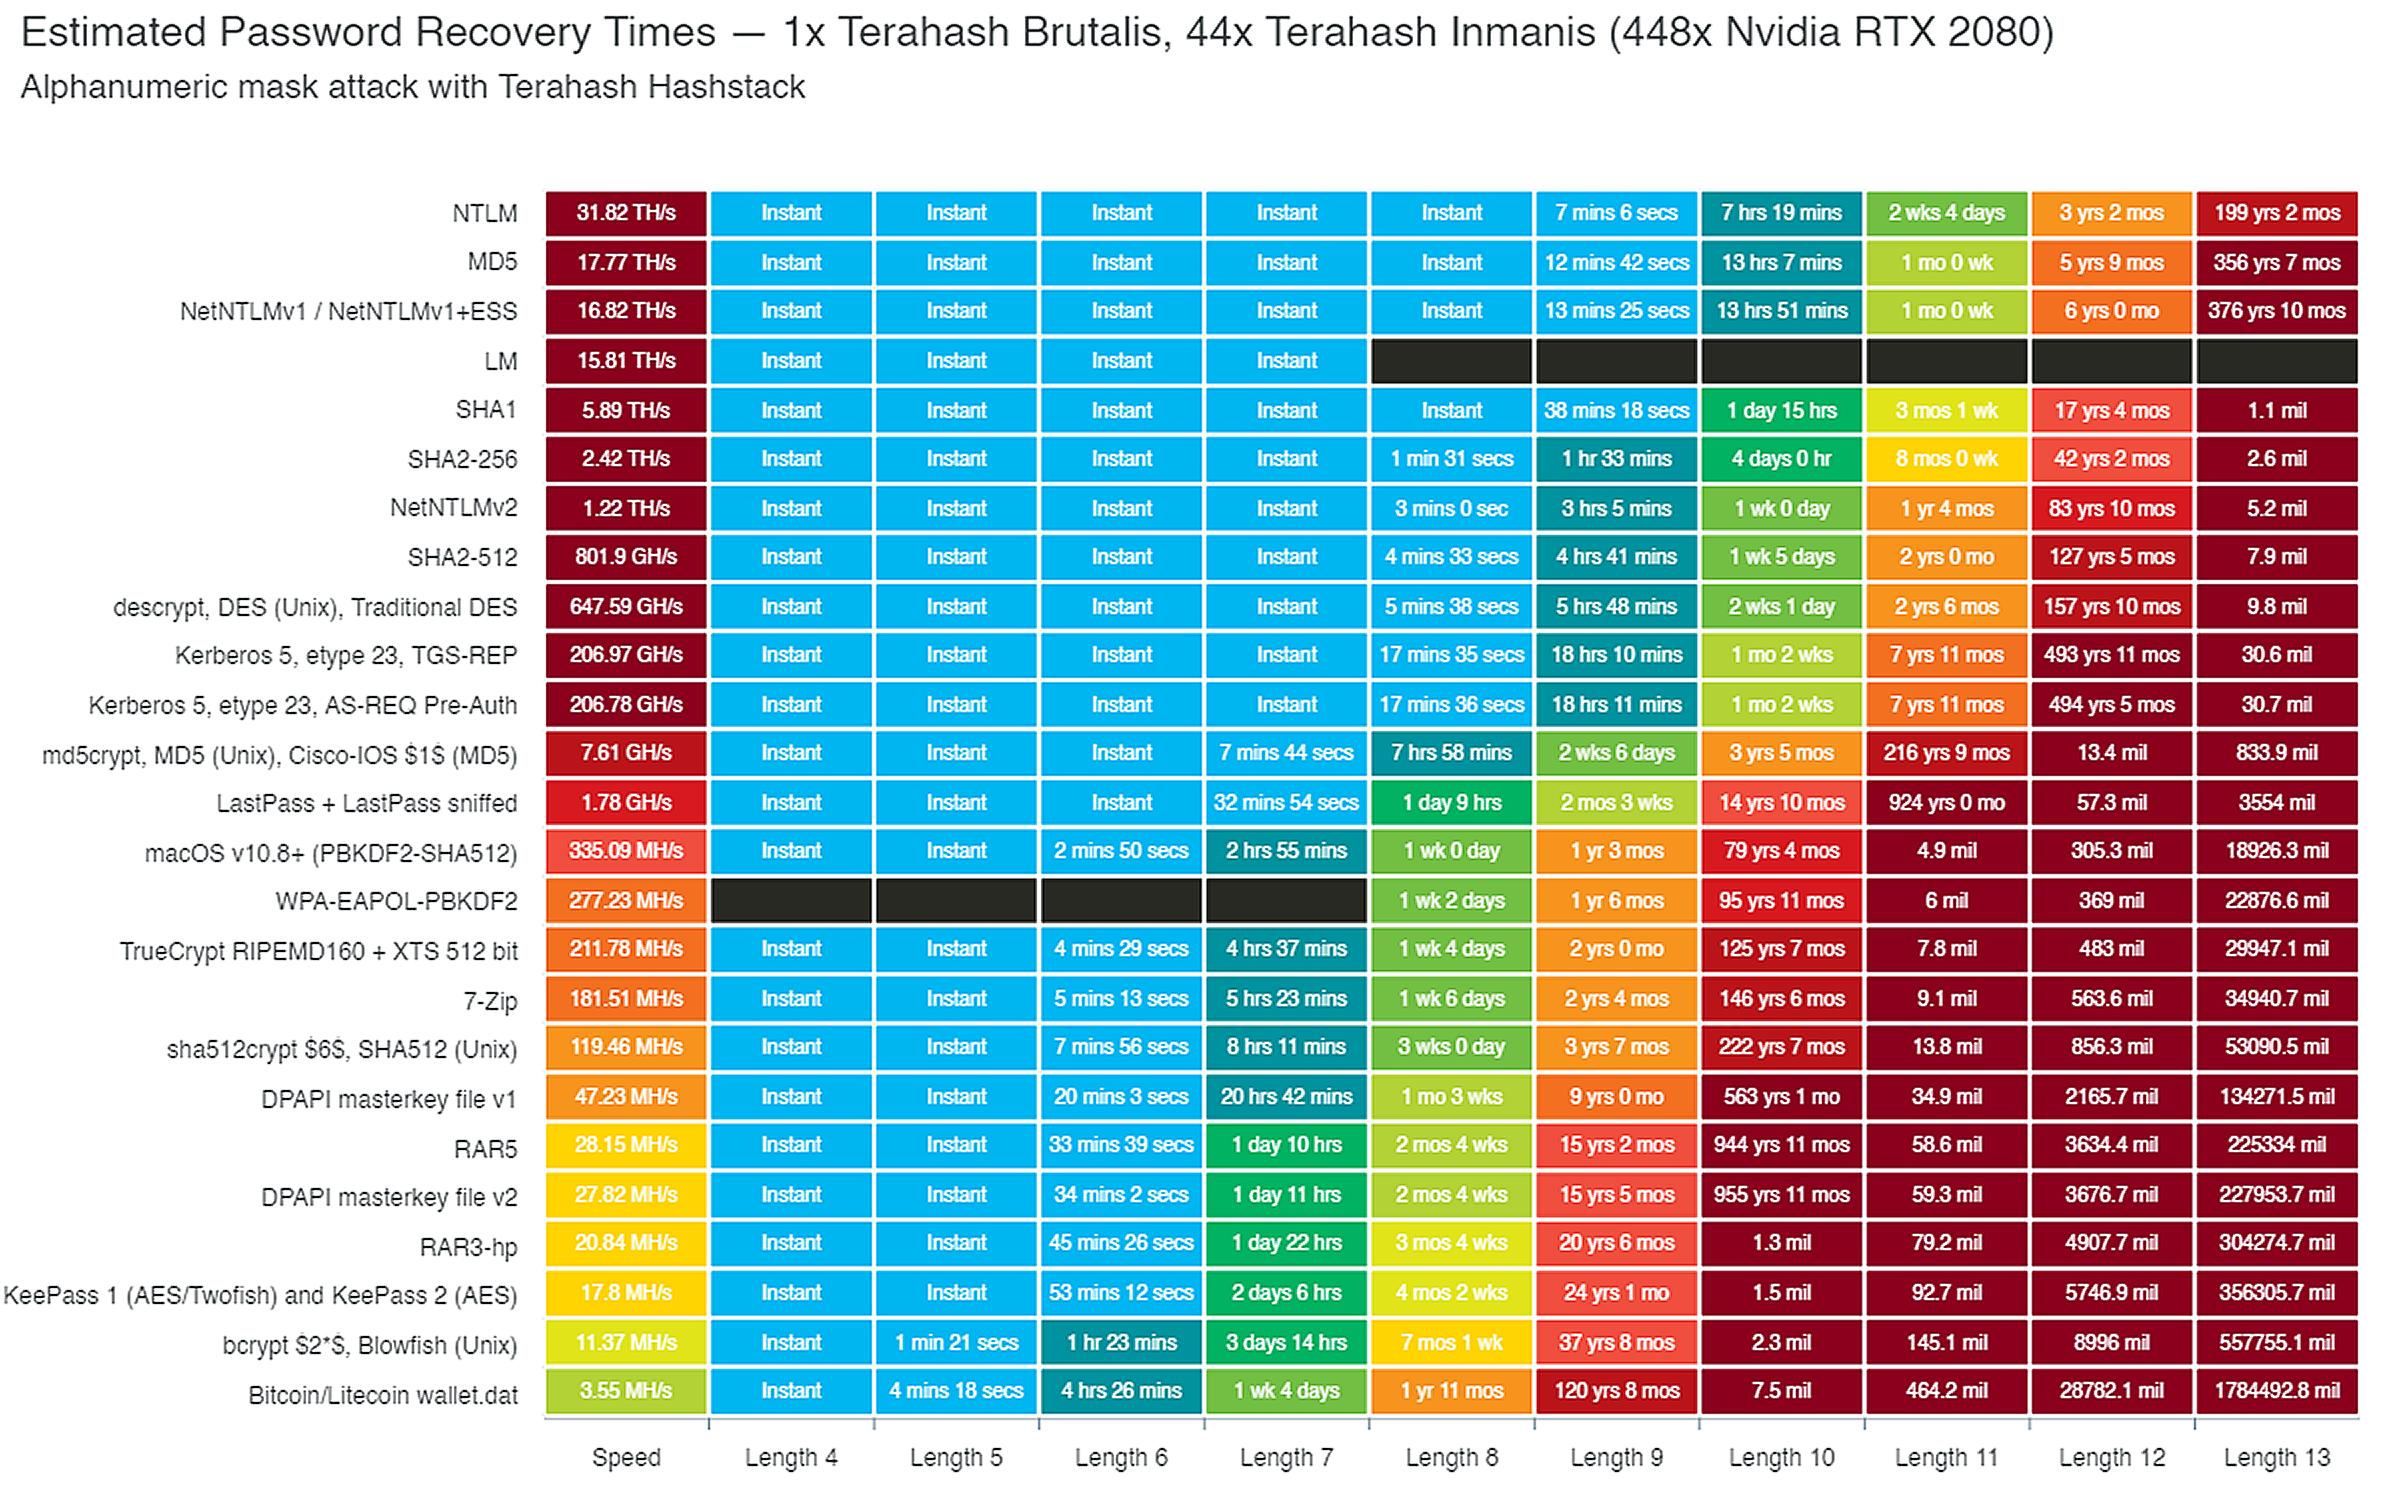
Many security frameworks such as NIST, COBIT as well as regulatory bodies such as PCI DSS, SOX, GLBA, HIPAA, etc have strict password complexity requirements. In order for Fortinet Fortigate firewalls to comply with those requirements, the Fotigate firewall can enforce strict password policies. Passwords are important. Password length and complexity IS equally important. Below you can see the chart showing recovery or cracking time based on the password type and length.
Here is a link to the NIST Requirements (Thanks to Adonis Sardiñas for providing me the info)
Basic Password Complexity
The Fortigate has some built-in features that you can enable that give you basic password complexity. This usually lets you comply with most necessary requirements.
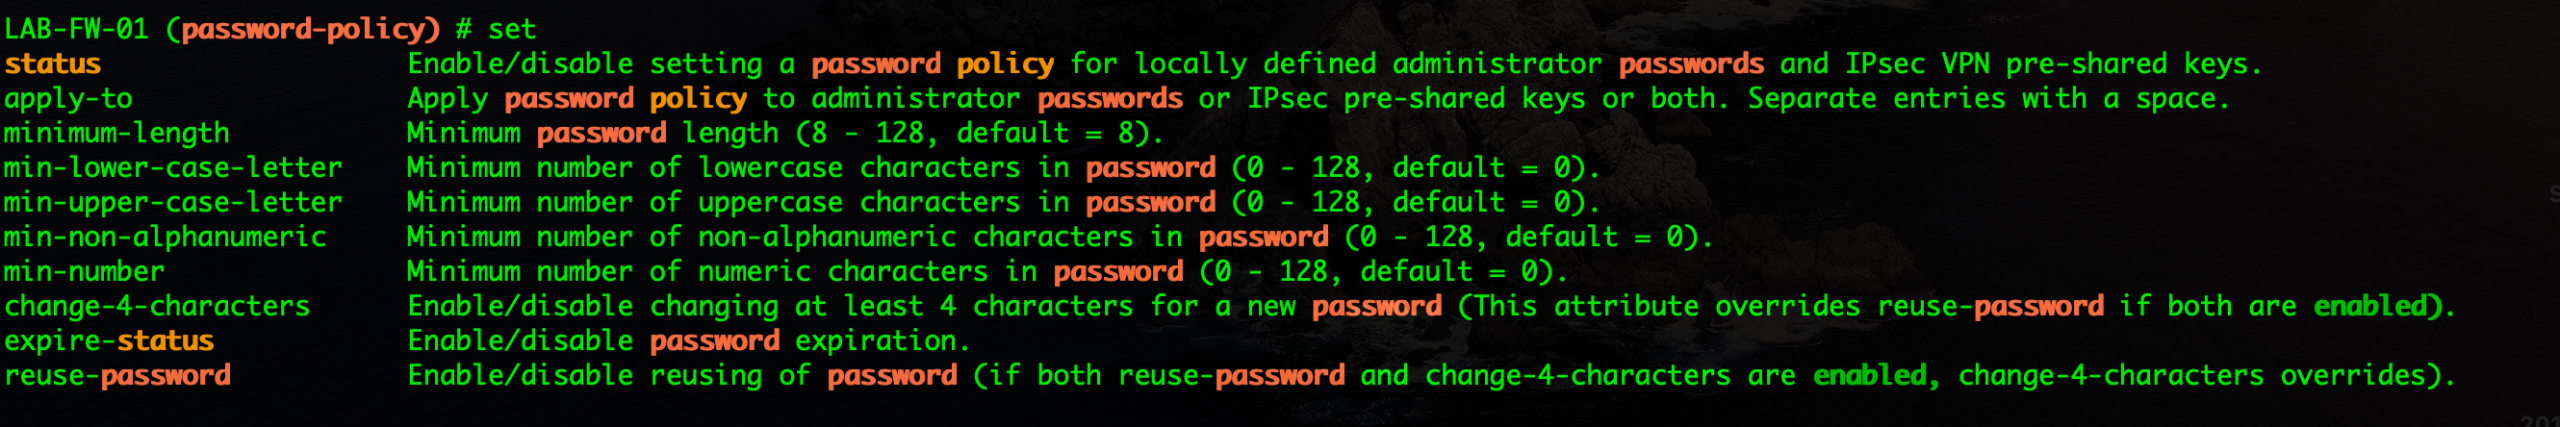
Here are your options. To get to this section, go to config system password-policy. Remember to use your set command.
apply-to – This option tells the Fortigate if you want to apply this profile to admin users, vpn users or both
minimum-length – How many characters are required for this password.
min-lower-case-letter – Here you can force a certain number of lowercase letters.
min-upper-case-letter – Here you can force a certain number of capital letters.
min-non-alphanumeric – This is the number of special characters
min-number – How many numbers are going to be part of the password.
change-4-characters – This is an interesting one. It comflicts with the re-use option but it protects from passwords that users/admins add 1,2,3, etc to the existing password. At least 4 characters need to be changed.
expire-status – If you want the password to expire, you first need to enable this by set expire-status enable and THEN you can ..
expire-day – Number of days after which passwords expire (1 – 999 days, default = 90).
GUI Option
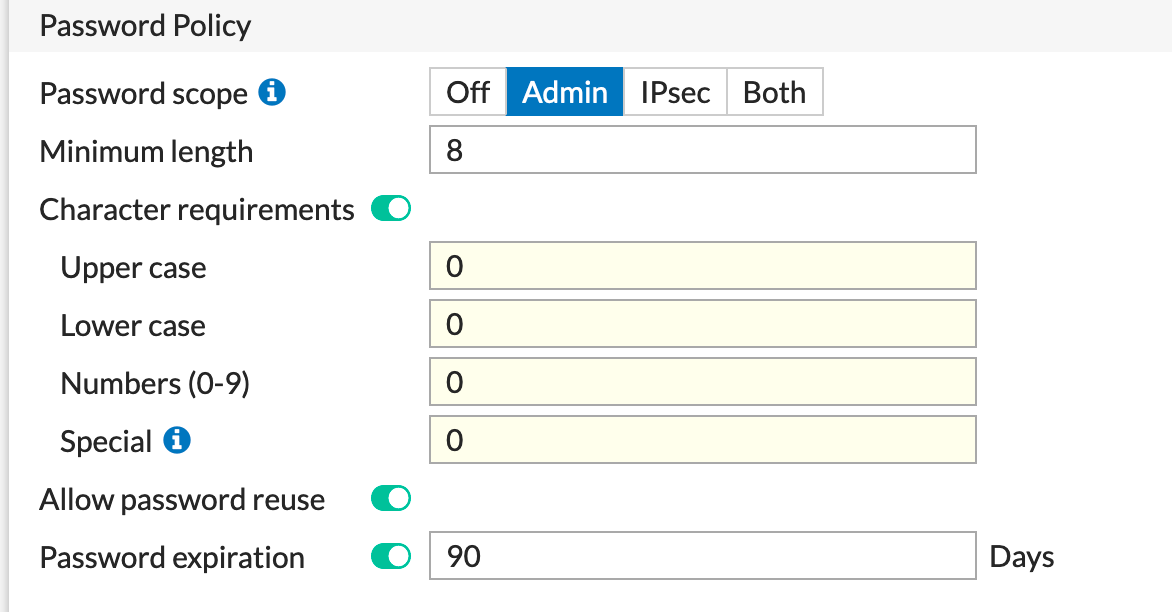
Some of the options are available via the GUI but not as granular as the CLI.
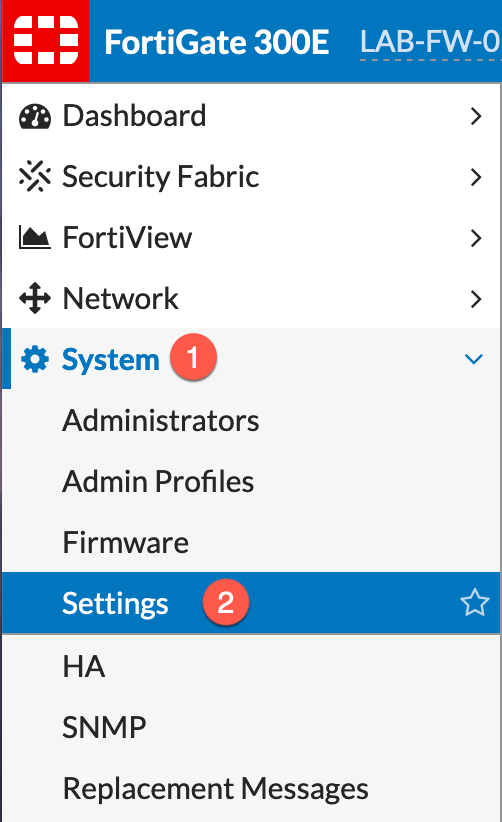
- System
- Settings
2-Factor Authentication for Administrators
Fortinet gives you two FortiTokens that you can use for testing and for the administrator account. Here is how we enable it.
config system admin
   edit yoirlen_admin
       set two-factor fortitoken
       set fortitoken FTKMOB8<REMOVED>
       set email-to yoirlen@<REMOVED>
   next
end
From the GUI, edit the admin user
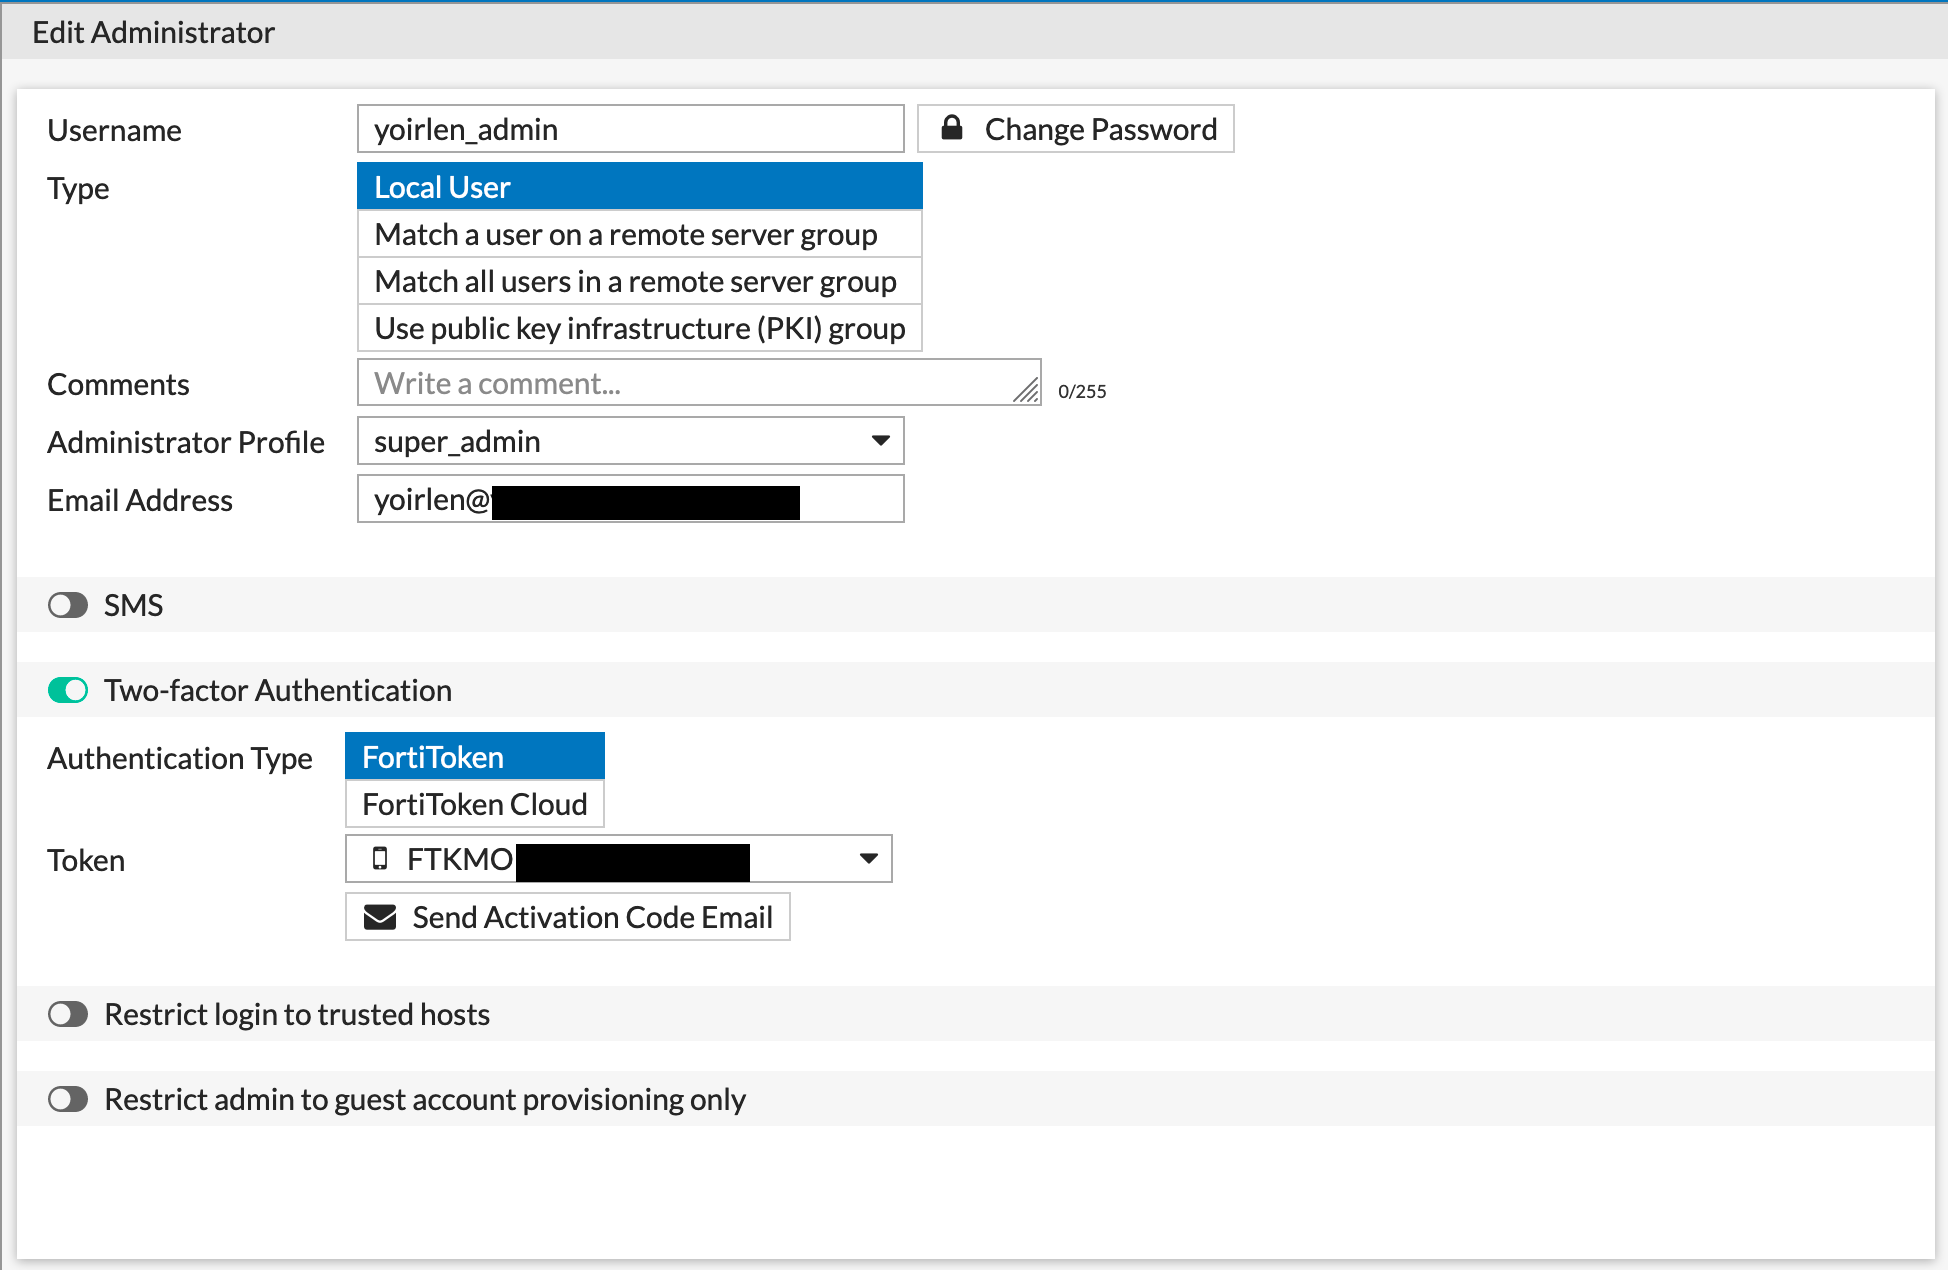
When you are in the cli and you type the set fortitoken and a ? you will get a listing of available Serial Numbers.
FTKMOB8<REMOVED>
FTKMOB8<REMOVED>
FTKMOB8<REMOVED>
FTKMOB8<REMOVED>
FTKMOB8<REMOVED>
FTKMOB8<REMOVED>
You can then copy and paste the token for the admin user.