In other articles, I have covered creating CA servers on Microsoft Windows and OpenSSL, here is an article using FortiAuthenticator. FortiAuthenticator or FAC is a versatile solution that can be used for RADIUS, Certificate Authority, 2FA, Guest Portal, BYOD portal.
Stay tuned to the monkey for additional FAC articles. I plan on doing an 802.1x, Guest Portal, 2FA, RADIUS & SSL VPN to name a few.
Creating the CA Certificate
Step 1 – Creating the CA Certificate
First, lets create the CA certificate pair.
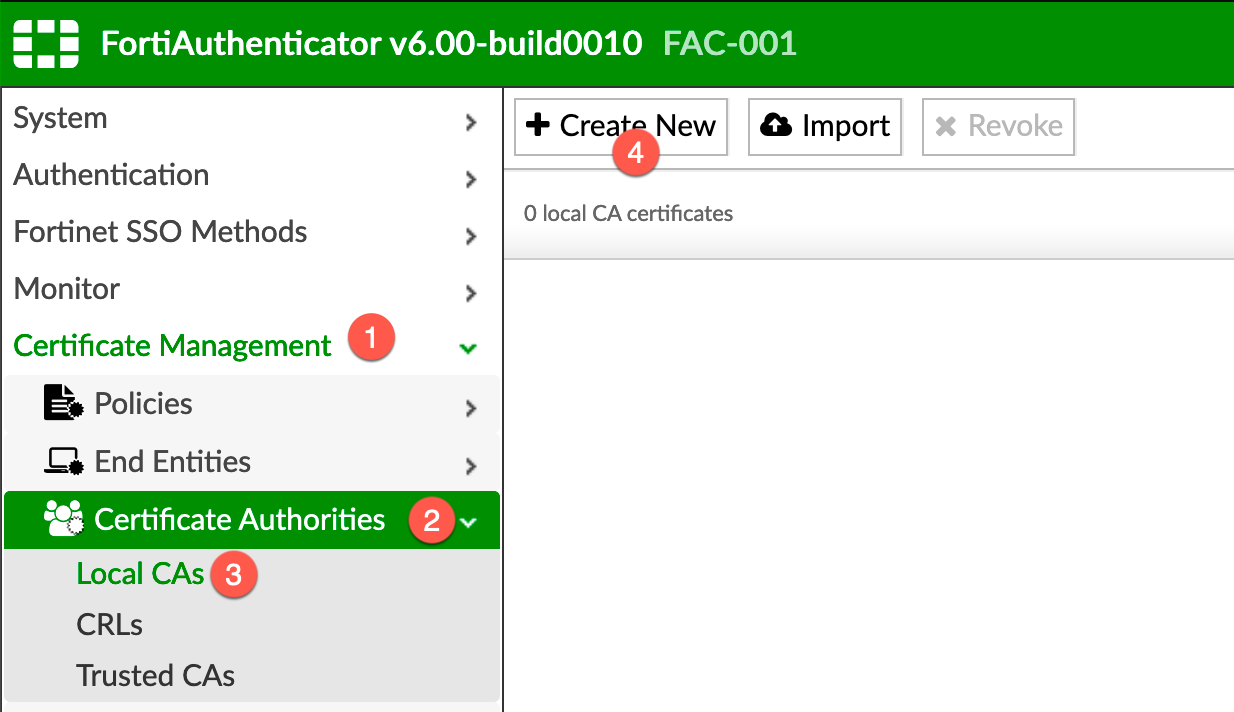
- Go to
Certificate Management - Then choose
Certificate Authorities - Choose
Local CAs - Then
Create New
Step 2 – Filling out the Certificate Attributes
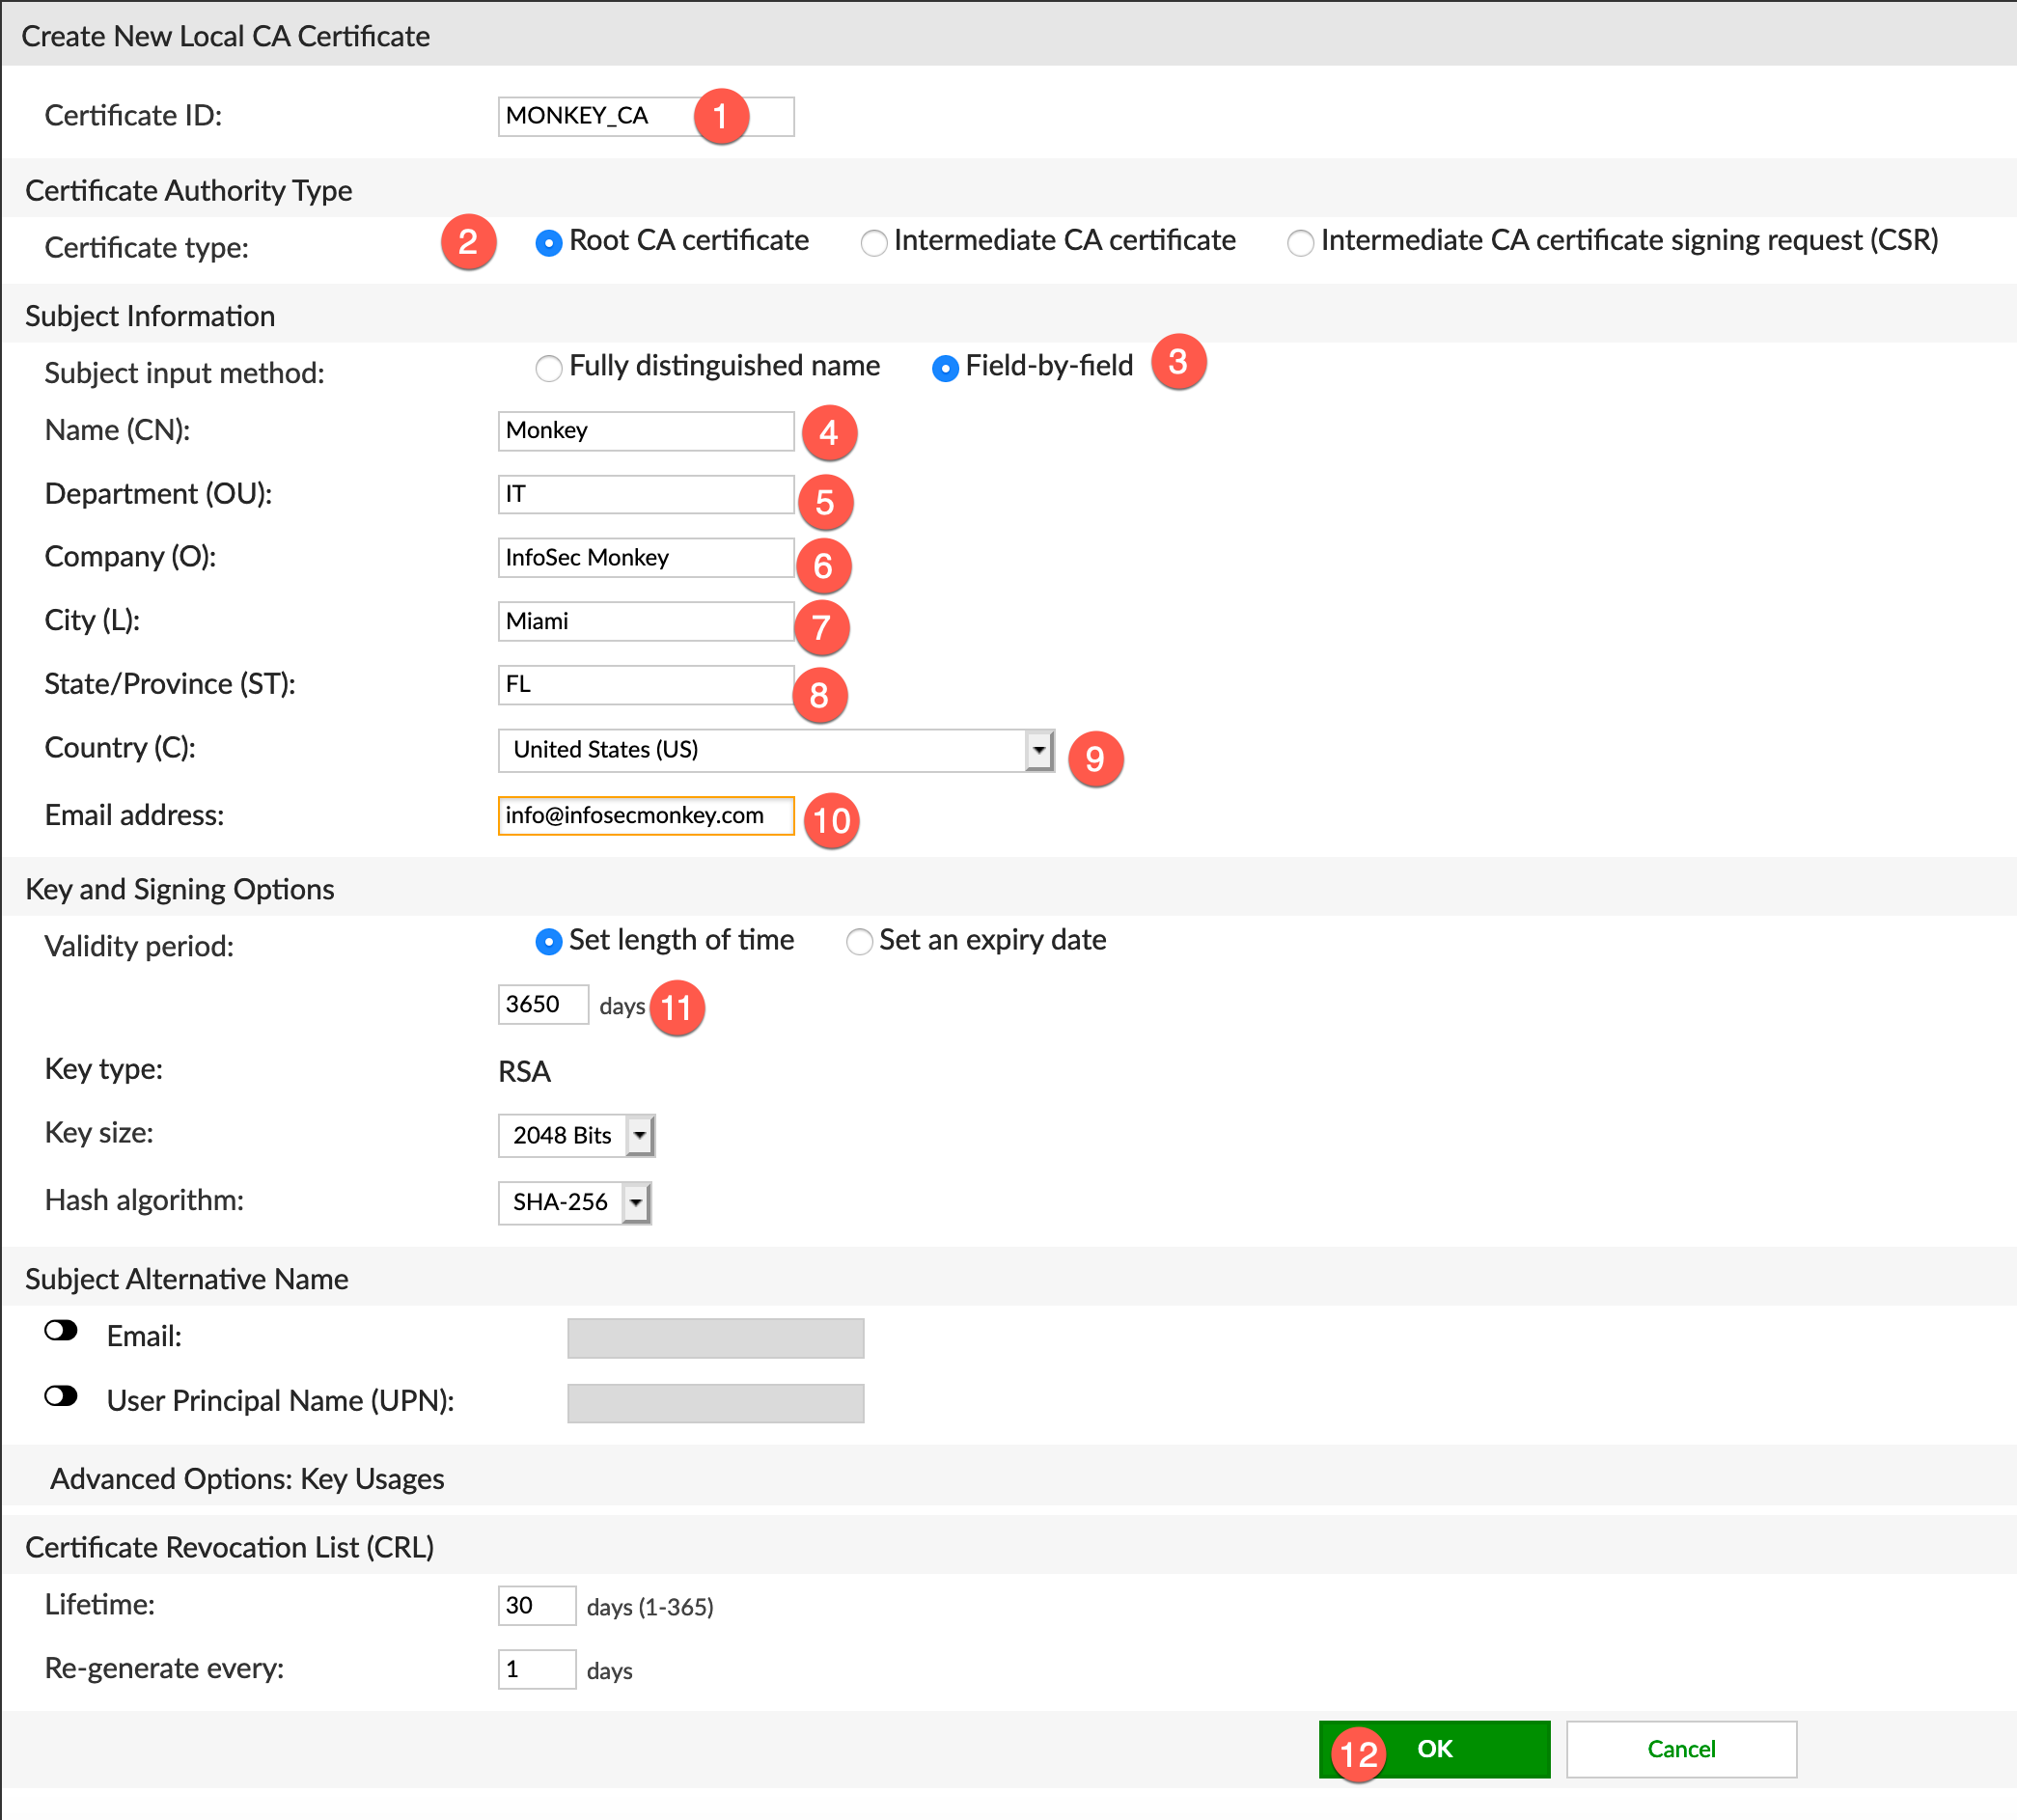
- Name the Certificate
- Make sure the
Root CA certificateis selected. - Choose
Field-by-field - Give it the CN (Common Name)
- Fill in the Department
- Fill in the Company Name
- Fill in the City
- Fill in the State
- Choose the correct country.
- Provide an email
- Choose the lifetime for the CA certificate. (3650 days = 10 Years)
- Choose OK.
Step 3 – Export Certificate

- Select the square box on the left of the CA name you created in
Step 2 - Then select
Export Certificate
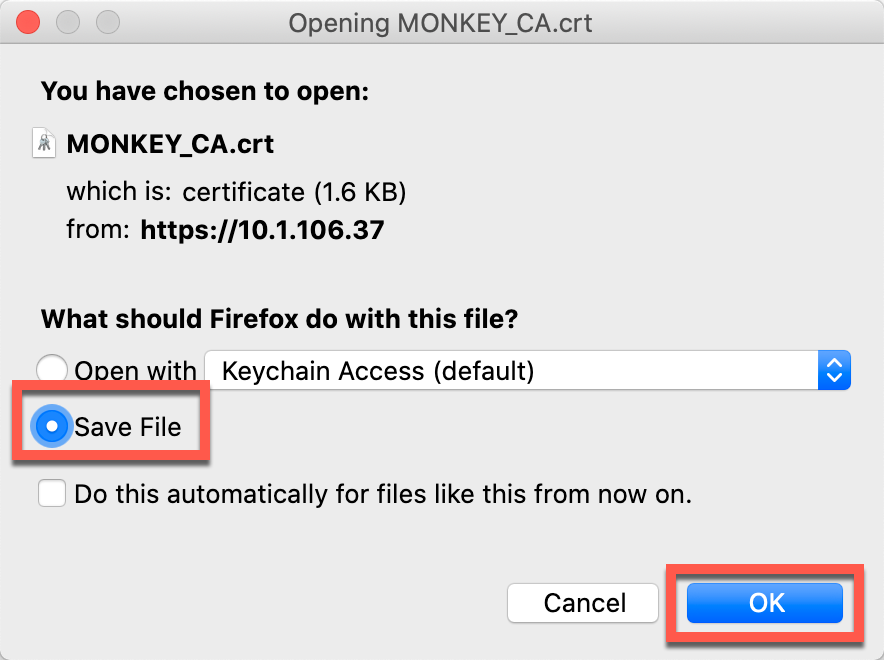
Step 4 – Validate Correct Format
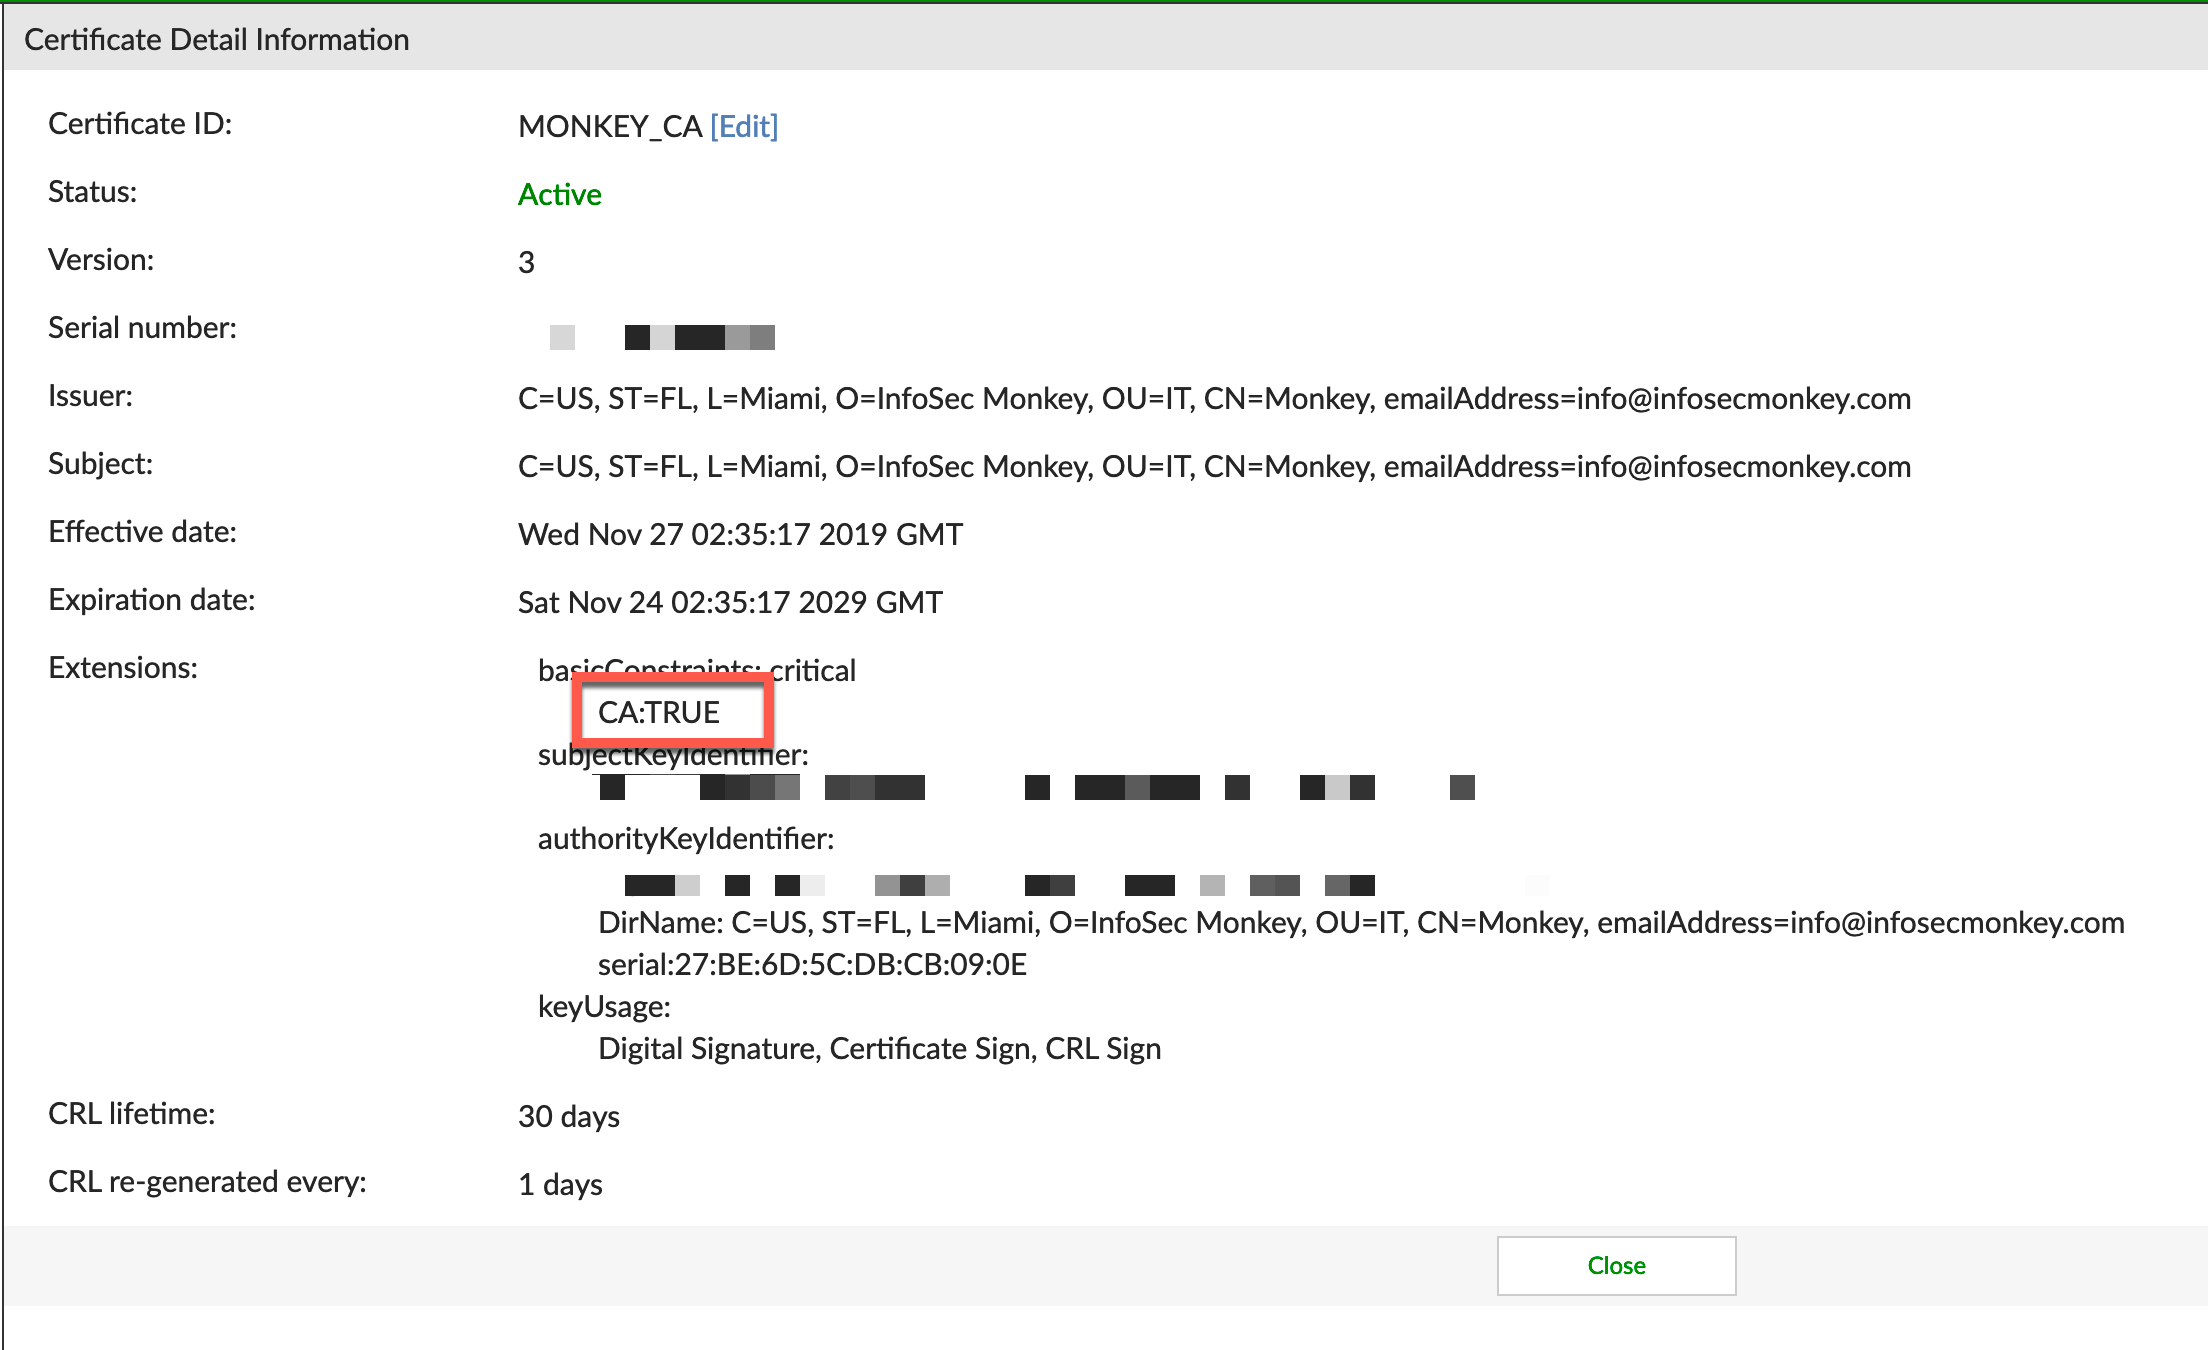
By NOT selecting the “square box” in step 3 and clicking on the certificate name, you will be able to see the details of the certificate. What you WANT to see is the CA:TRUE
Hope this helps