By Manny Fernandez

March 15, 2019

Configuring Custom NTP Server on Fortigate

Configuring Custom NTP Server on Fortigate

The Fortigate firewall comes pre-configured to use the Fortiguard time sources via NTP.  You can also configure the Fortigate to act as a time source for different LANs on the Fortigate.  To use your own NTP servers, you will need to head to the CLI to make the changes.

CLI Configuration
config system ntp
set type custom  (This must be enabled first)
set ntpsync enable
config ntpserver
edit 1
set server X.X.X.X
next
edit 2
set server Y.Y.Y.Y
next
end
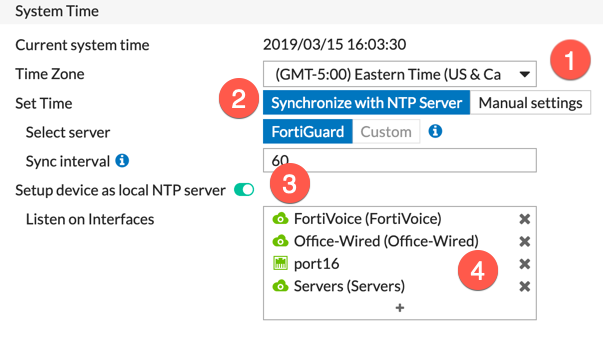
NTP

1 – Set your ‘Time Zone’

2 – Ensure that you have Synchronize with NTP Server.

3 – To allow hosts on a particular interface to use the Fortigate as a time source, you need to enable this radio button.

4 – Select the interfaces that will participate in the ‘Time Source’ process.
Legacy Protocols Must Die: FTP, Telnet, HTTP, and Their Secure Replacements

Legacy Protocols Must Die: FTP, Telnet, HTTP, and Their Secure Replacements

Replace legacy protocols like FTP, Telnet, and HTTP with secure alternatives. Get the exact configs for FortiGate, Linux, and macOS to harden your network.

Read More
The Most Common USB Plugs and Their Names: A Practitioner’s Field Guide

The Most Common USB Plugs and Their Names: A Practitioner’s Field Guide

Identify USB plug types and names for Type-A, B, Mini, Micro, and C. Learn real-world speeds and use cases to pick the right cable...

Read More
Know Your Plugs: A Practitioner’s Guide to Common AC Connectors

Know Your Plugs: A Practitioner’s Guide to Common AC Connectors

Identify NEMA and IEC AC connectors for safe power setups. Learn plug ratings, use cases, and limitations to prevent rack outages and equipment damage.

Read More