
Have you ever had an IPS signature that continues to trigger falsely? In case you did not know, we call that a false positive . These are bad, but worse yet would be a false negative but that will be covered on another article. For now, lets fix that noisy IPS signature that floods our emails with alerts or worse yet, blocks legitamte traffic.
To have a false positive in your environment, the assumption is that you already have an IPS policy that is triggering, so I will not go over configuring IPS. In my scenario, we have a server on the inside 10.1.1.1 that is triggering a particular IPS signature when communicating to an IP on the Internet 12.1.1.1. I will create an IP exemption list which will change the outcome of that traffic when it gets triggered.
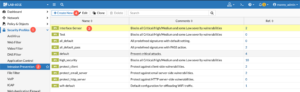
Go to you IPS profile by clicking on (1) Security Profiles then click (2) Intrusion Prevention , then choose your policy, in my case (3) Interface-Sensor and then (4) Edit.
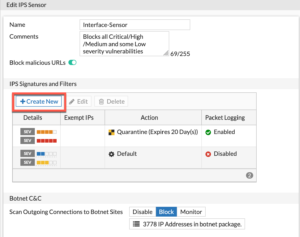
Once you are inside your profile, you will see that configuration. You will then choose IPS Signature and Filters and choose Create New.
You will now choose the Signature button on the top of the screen.
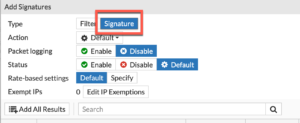
You can now see the signatures for the IPS. You should either search by name, or if you have a lot of extra time, scroll through the list until you find the signature(s) you are looking for.
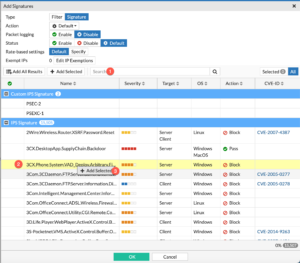
In my example, I choose a random signature:
3CX.Phone.System.VAD_Deploy.Arbitrary.File.Upload
Once there, you can right click on the signature and click the Add Selected.
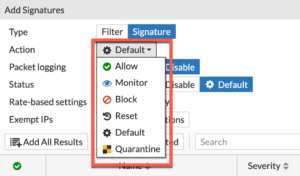
Now you will be able to choose the disposition for this signature when it matches the IP exemption(s) list. Remember that Monitor will Allow but will also log.
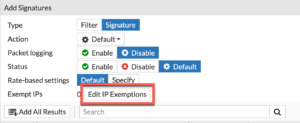
Now we will add the Exemption by clicking the Edit IP Exemptions
You can now add one or multiple sets of source and destination depending on where it is triggering.
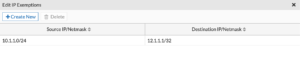
As you can see in the screenshot, you can see the source and destination IPs in my example.
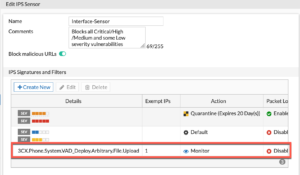
In the screenshot, you can see that I have the signature in question, is now set to Monitor instead of Default and you can see that in the Exempt IP column, we can see a value of 1 .
Hope this helps.


