
By Manny Fernandez

October 10, 2021

Quick Tip – Controlling Source Interface Traffic

Quick Tip – Controlling Source Interface Traffic

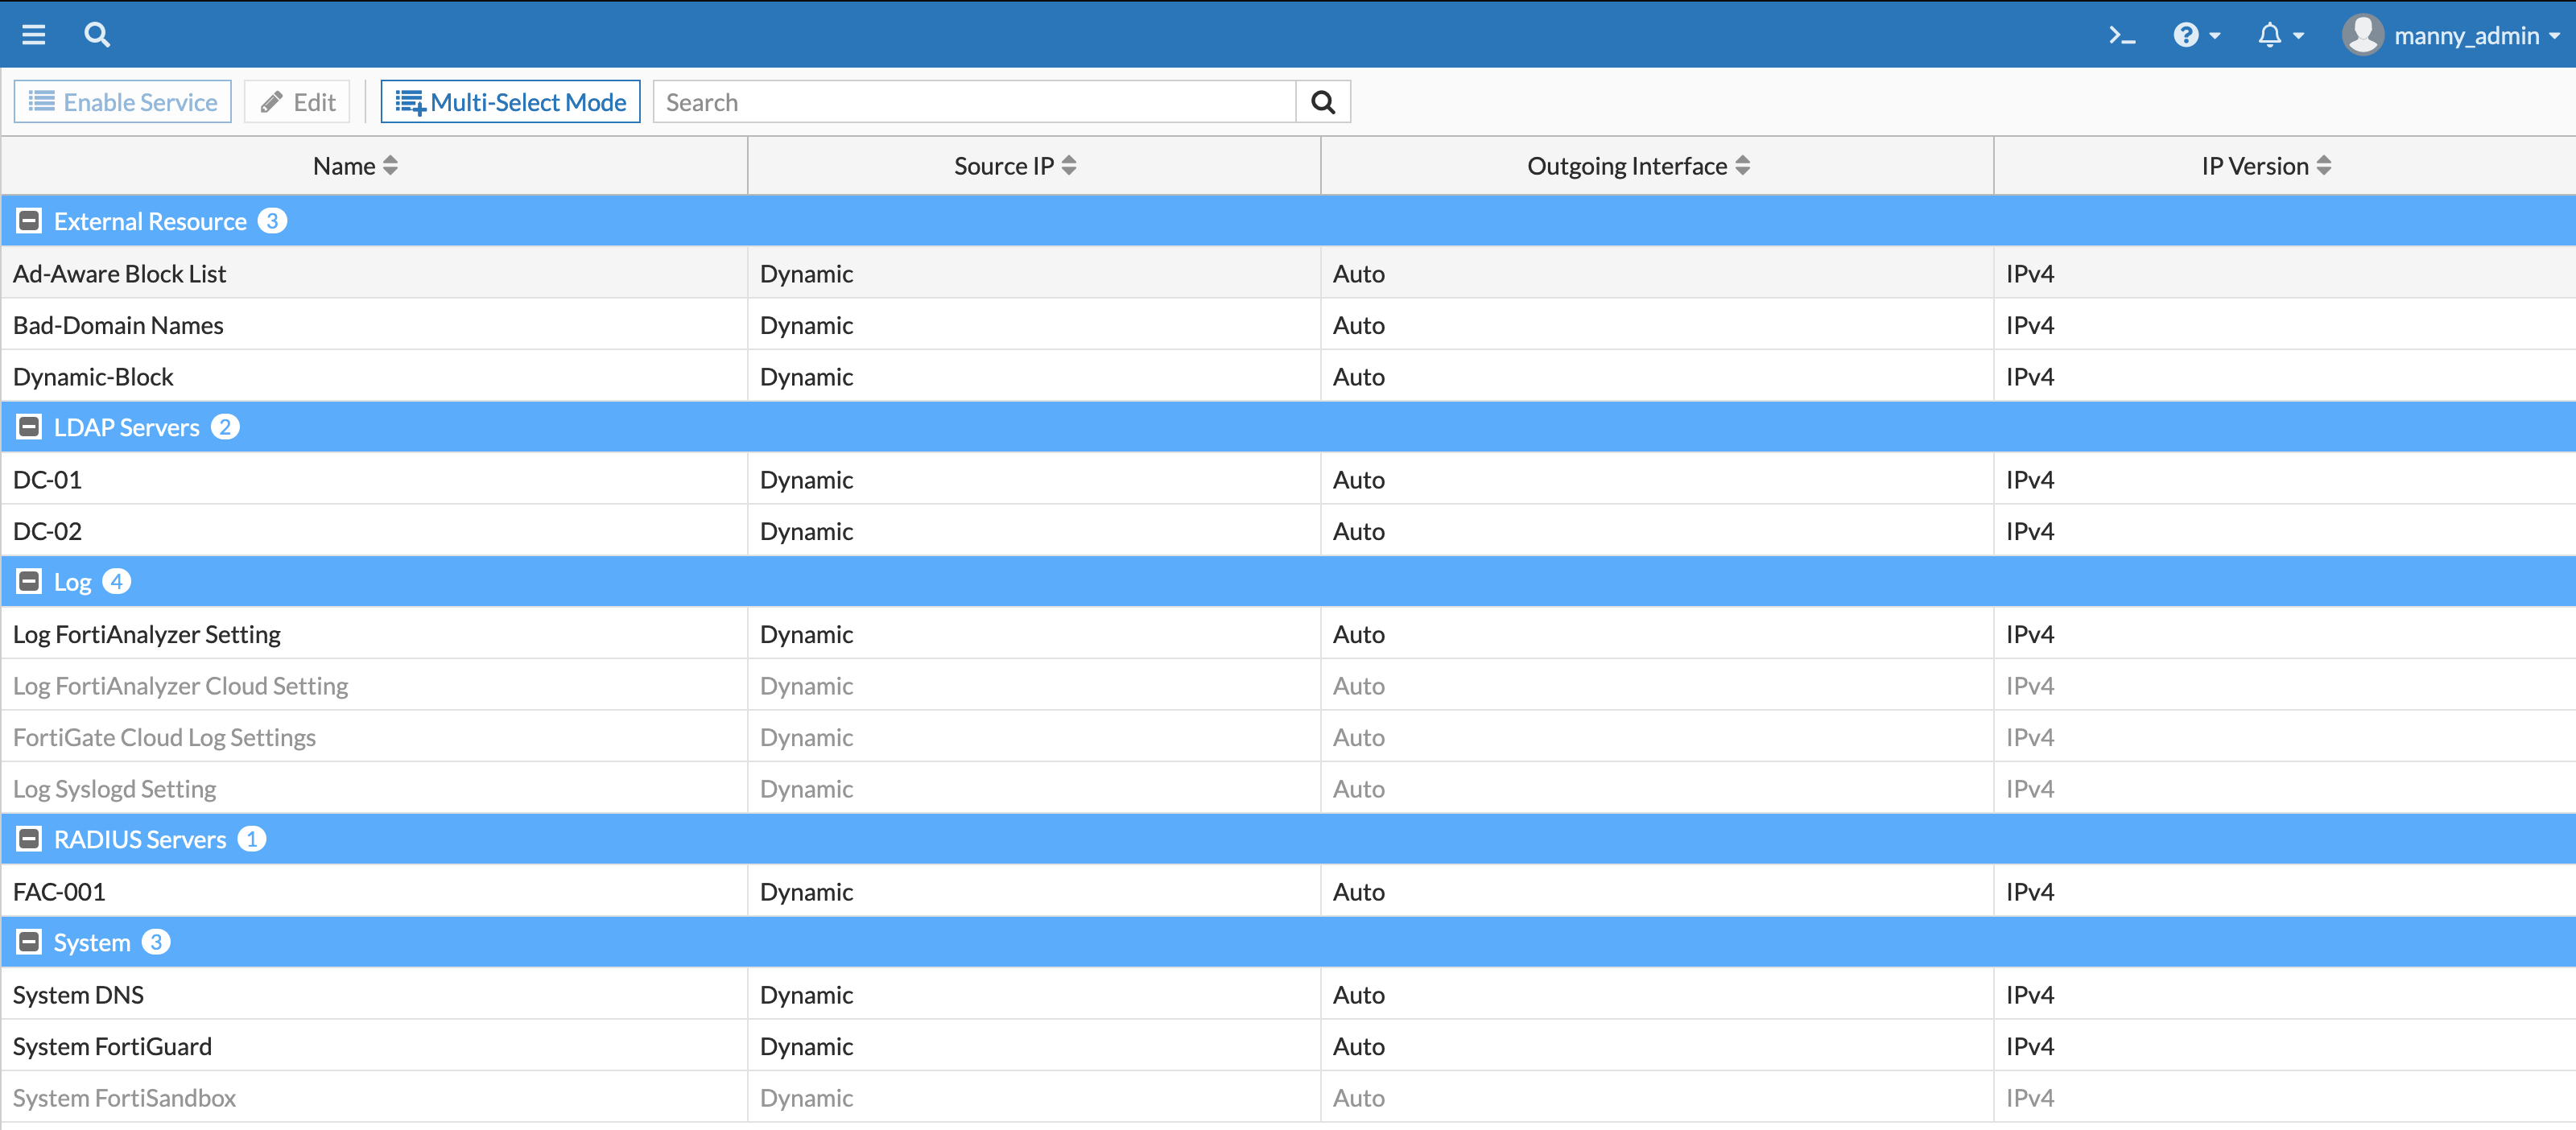
In version 7.x of FortiOS there is now a GUI based option that can allow you to choose what interface the traffic will egress from.
2021-10-10_14-25-05

As you can see above, you can choose source IP and interface for the various functions such as the External Resources which are the external URL dynamic lists that can be created on the FortiGate.  Also the FortiGuard labs connections.
2021-10-10_14-25-37

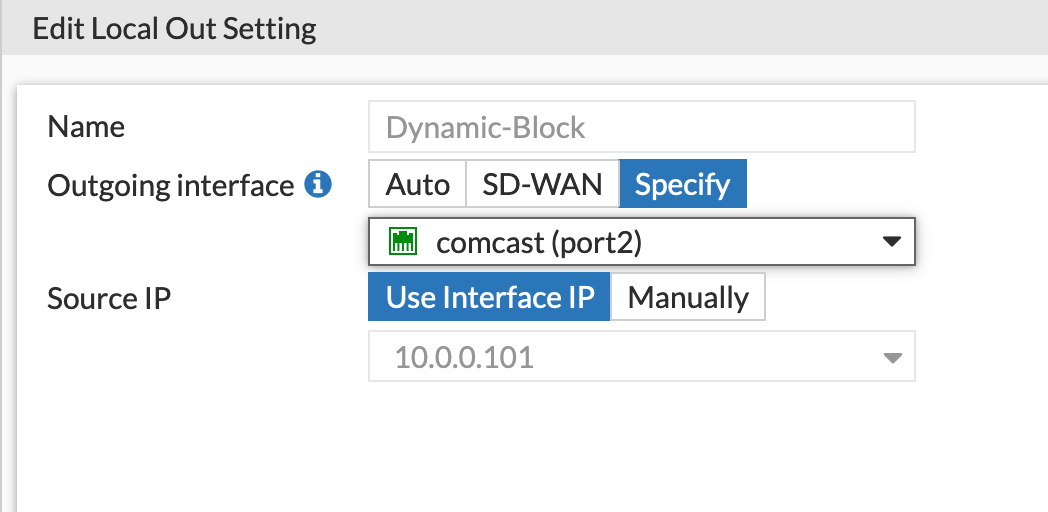
Above we can see the Dynamic Block which is an External Resource to use Comcast Circuit which is my port2.
2021-10-10_14-25-59

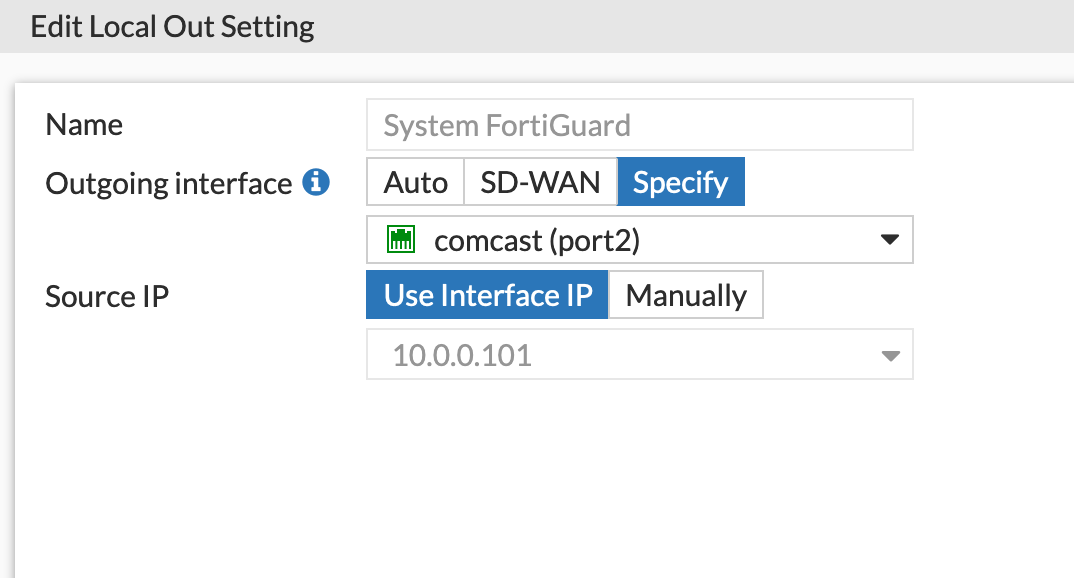
Above we can see the FortiGuard Labs connection.

As you can see in both examples, you can choose the Source IP that is automatically assigned to the interface selected, or you can choose to manually assign one.

Hope this helps.

 

VRF Explained: Virtual Routing and Forwarding on FortiGate, Cisco and Juniper

VRF Explained: Virtual Routing and Forwarding on FortiGate, Cisco and Juniper

Learn virtual routing and forwarding (VRF), then build VRFs and route leaking on FortiGate, Cisco IOS XE and Juniper Junos with tested CLI.

Read More
FortiGate IPAM vs DHCP: Differences, Overlap, and What to Check Before You Turn IPAM On

FortiGate IPAM vs DHCP: Differences, Overlap, and What to Check Before You Turn IPAM On

FortiGate IPAM vs DHCP explained: what each one assigns, where they overlap, and what to check before enabling IPAM so it does not renumber...

Read More
Outlook CVE-2026-124194: Patch the Zero-Day That Leaks NTLM Hashes

Outlook CVE-2026-124194: Patch the Zero-Day That Leaks NTLM Hashes

Outlook CVE-2026-124194 leaks NTLMv2 hashes from one opened .msg file. Check fixed builds, force the Office update, and block SMB egress on FortiGate.

Read More

