* Sometimes you may want to use a certificate to authenticate to you Fortigate firewall. This is a simple process that requires a two different pieces; the SSH key on you machine and the user on the Fortigate. For this example, I am going to use SecureCRT from VanDyke Software. I have used SecureCRT for years. I used it when I ran Windows as my primary desktop OS, then I went to Linux for 8 years and ran it there, and now that I am on the Mac, I use it here. You can do the same via the CLI on MacOS and Linux however Windows will be somewhat of a challenge due to the non-native SSH support.
Lets get started:
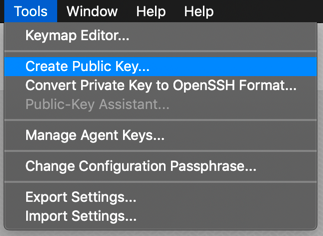
In SecureCRT, click on Tools, then choose ‘Create Public Key’
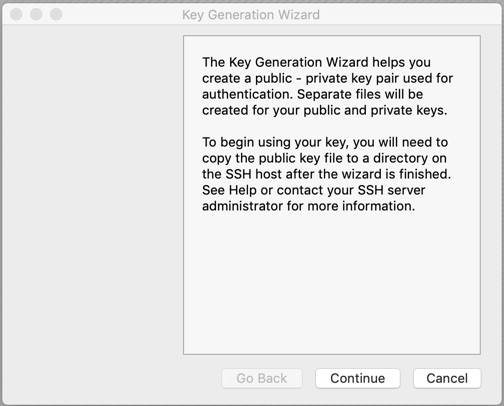
Once there, choose to generate a key pair and choose ‘Continue’
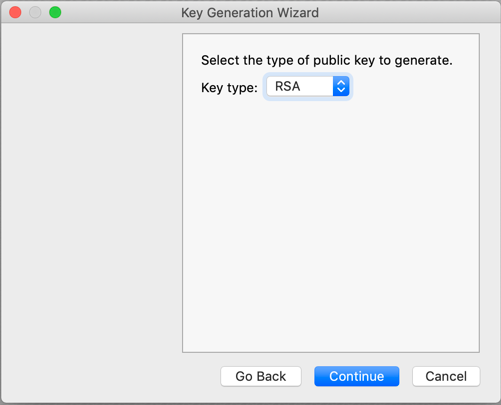
Choose ‘RSA’ from the drop down
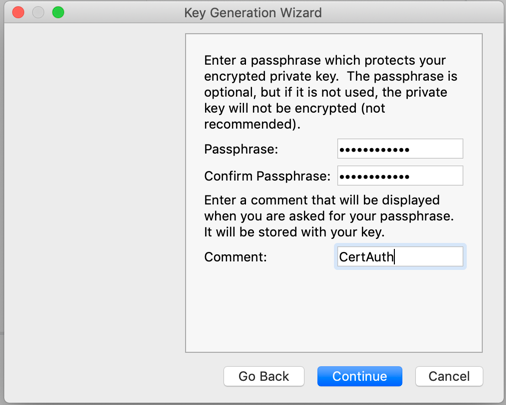
Now, choose a passphrase and a Comment.
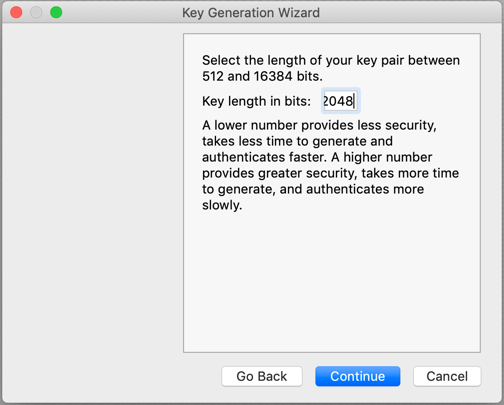
Choose a key length and continue
Now choose the format of the key. Even though the screenshot shows the SecureCRT format, I use the ‘OpenSSH Key Format (new)’. Tell it where to save the file.
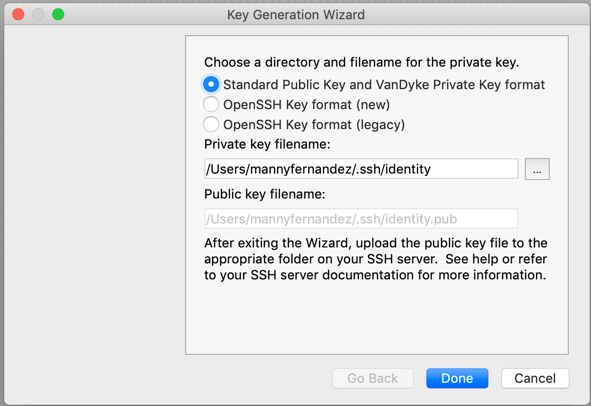
Note that by default, there will be a ‘identity’ and an ‘identity.pub’, obviously the .pub is your public key while the other is you private key.
Now for the Fortigate side of the house.
config system admin
edit "monkey"
set accprofile "super_admin"
set ssh-public-key1 "ssh-rsa AAAAB3NzaC1yc2EA < REMOVED FOR BREVITY > yYKZXrwGd"
next
end
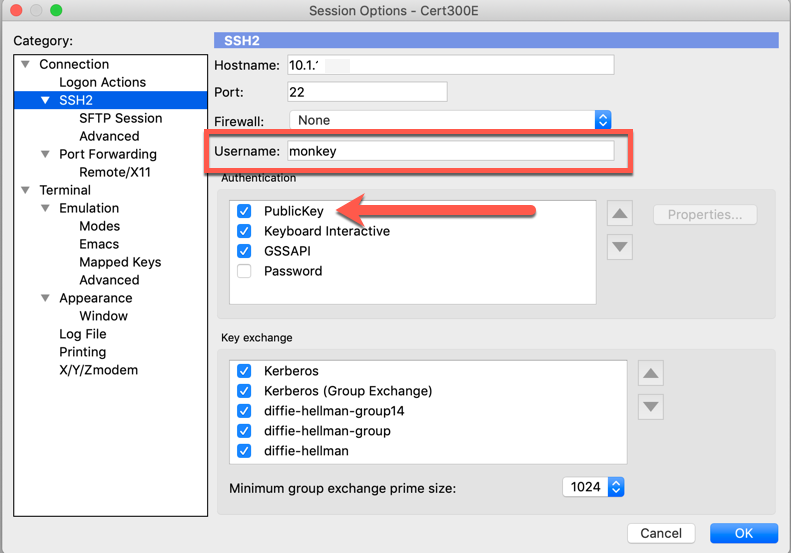
Finally, you need to create a session on SecureCRT that uses the certificate.
Hope this helps