
When you connect to a FortiGate in Web Portal mode, by default, you are able to create bookmarks using HTTP/HTTPS, FTP, CIFS/SMB, RDP, SSH, TELNET, VNC, Citrix, etc. However, you may not want the users to be able to use all of these protocols to connect to devices inside your network.
Use Case
You have users that connect, and you ONLY want to give them access to HTTP/HTTPS and SSH. You do NOT want them using any of the other protocols to create bookmarks.
FortiGate Default Settings
First, lets take a look at the defaults
In this snippet, you can see that there are no limitations to the access the user gets. It is hard to imagine where it will rest when we configure it, however once you see it in the working snippet, you will be able to identify the missing code on this one.
config vpn ssl web portal
    edit "web-access"
        set web-mode enable
        set forticlient-download disable
        config bookmark-group
            edit "gui-bookmarks"
               config bookmarks
                   edit "Observium"
                      set url "http://10.1.106.50"
                   next
                   edit "Calibre Books"
                      set url "http://10.1.105.7:8080"
                   next
                end
            next
         end
     next
end
Here is what the user sees when they connect to the VPN
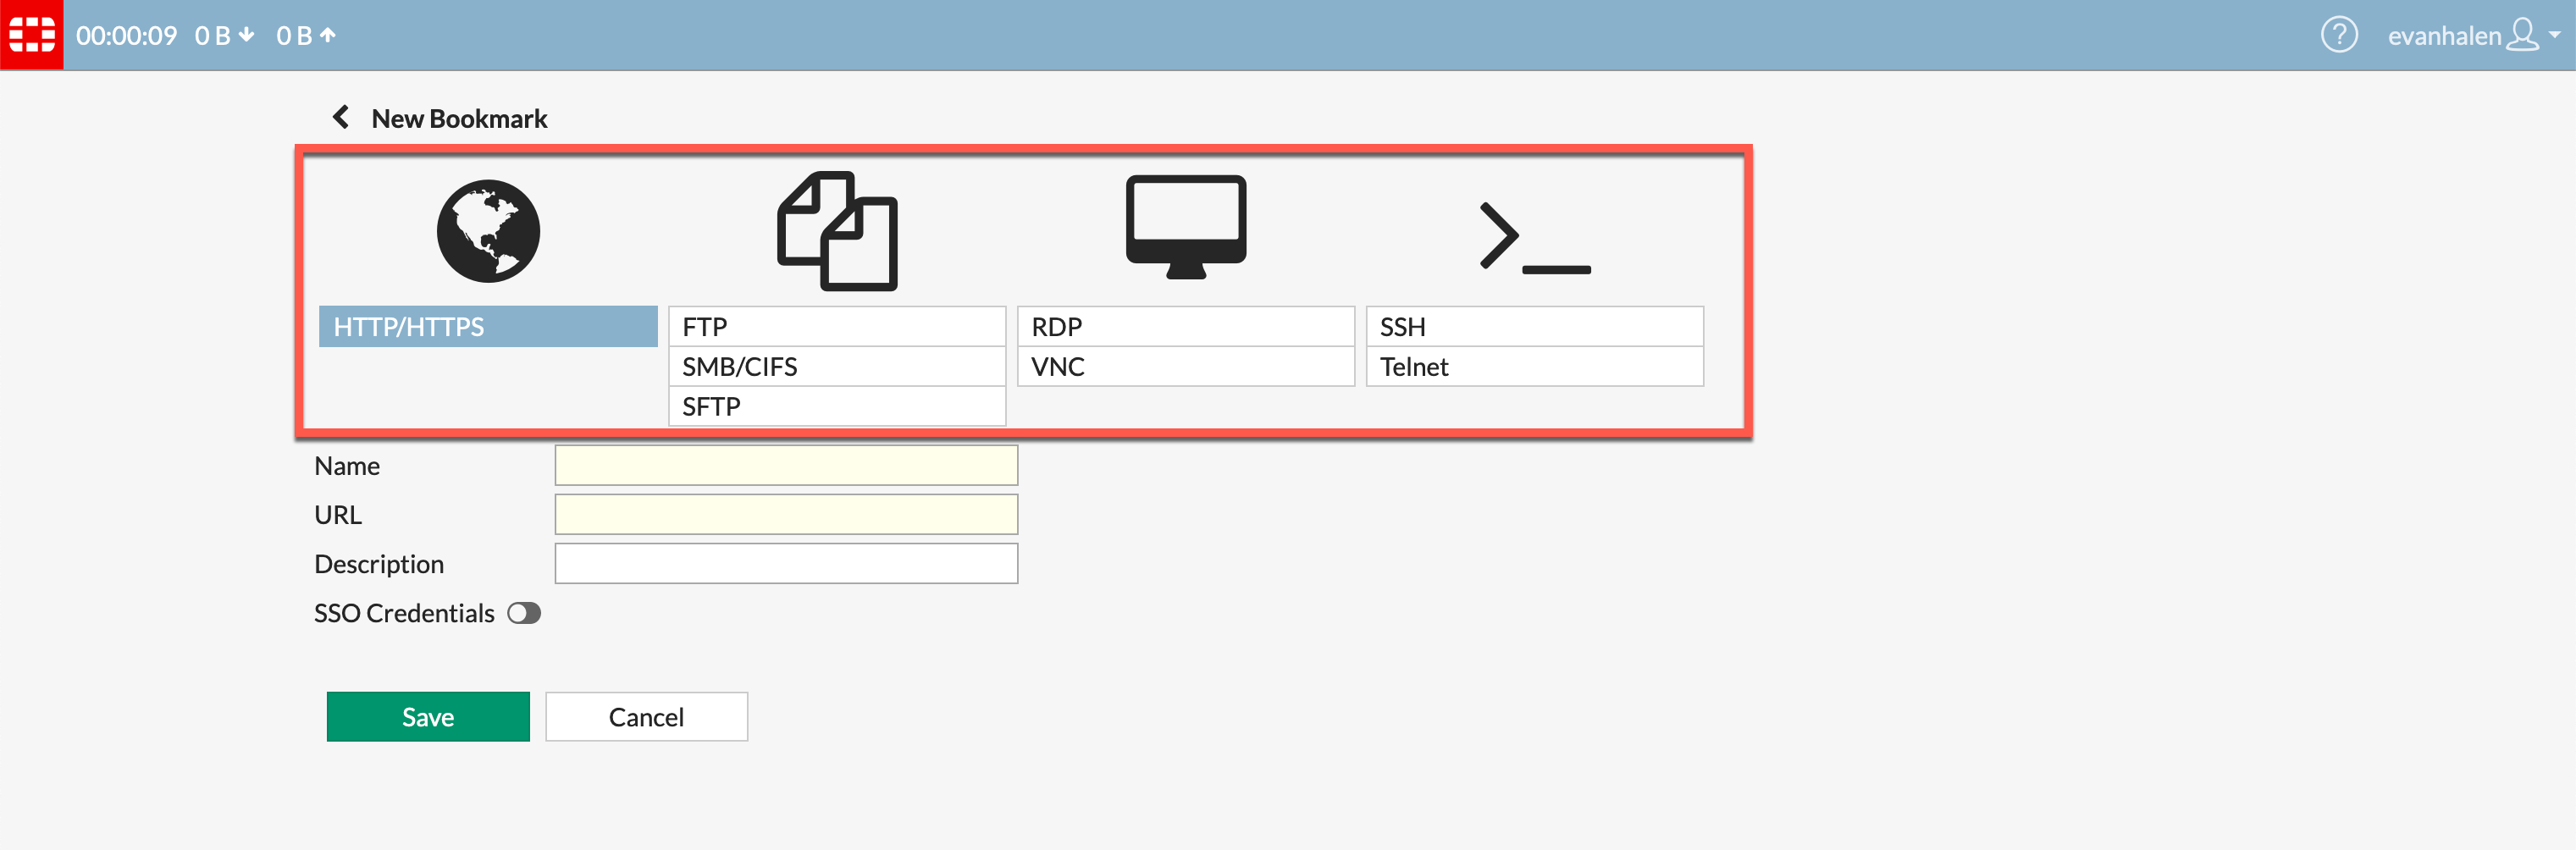
Here you can see that the user evanhalen can create personal bookmarks using a number of protocols. In my use case, we wanted to limit them to HTTP/HTTPS and SSH.
FortiGate Limited Access Config
Here we have the modified config. I have highlighted the modification in red. NOTE: Your portal name may be different. I am using the default one but your mileage may vary.
config vpn ssl web portal
    edit "web-access"
        set web-mode enable
        set allow-user-access web ssh ping
        set forticlient-download disable
        config bookmark-group
            edit "gui-bookmarks"
                config bookmarks
                    edit "Observium"
                       set url "http://10.1.106.50"
                    next
                    edit "Calibre Books"
                       set url "http://10.1.105.7:8080"
                     next
                  end
               next
          end
     next
end
Once this is saved, you can see that the user is not limited in what they can create.
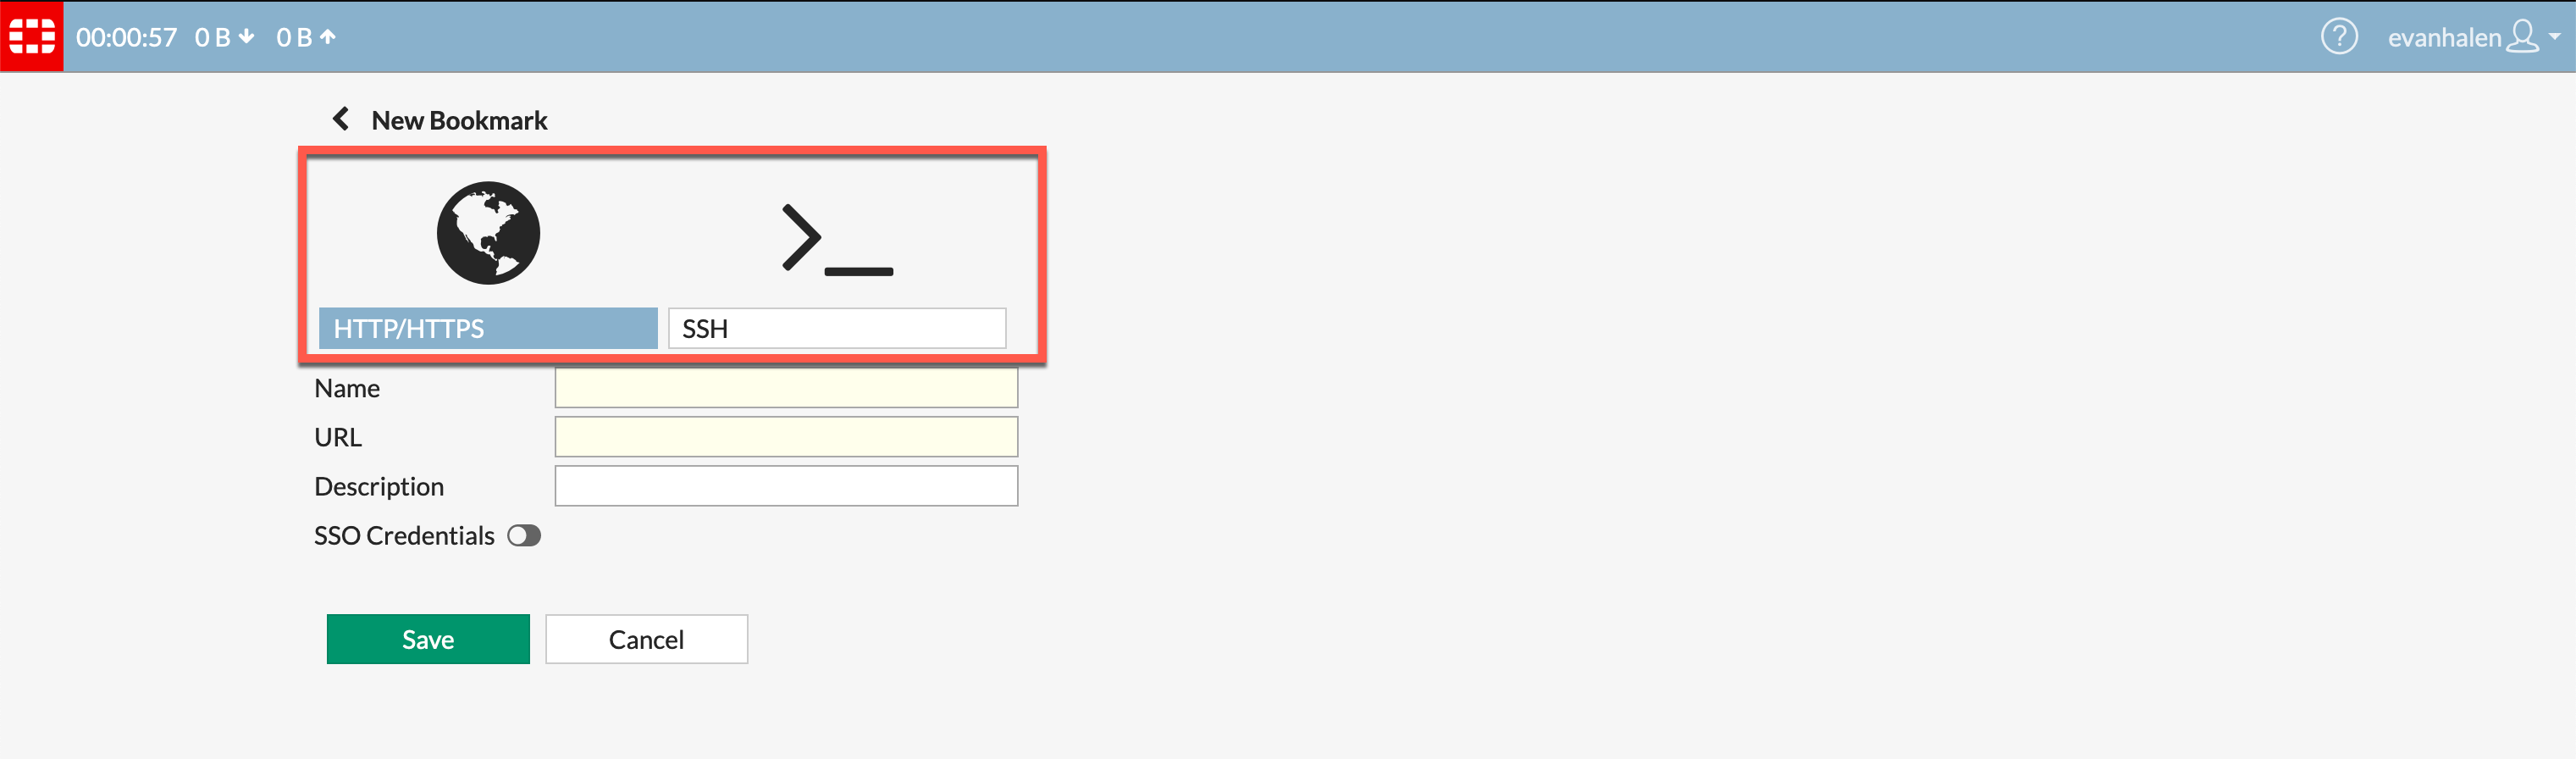
We can see that the user can now ONLY create HTTP/HTTPS and SSH bookmarks.
Hope this helps.


