By Manny Fernandez

November 19, 2019

DNS over TLS (DoT) on the Fortigate

DNS over TLS (DoT) on the Fortigate

I recently wrote an article about the difference between DNS over HTTPS and DNS over TLS and the differences between the two.   Now as promised, I will show how to configure DoT.  Lets get started.

Requirements: FortiOS 6.2x

As stated above, you require 6.2x to configure this feature.
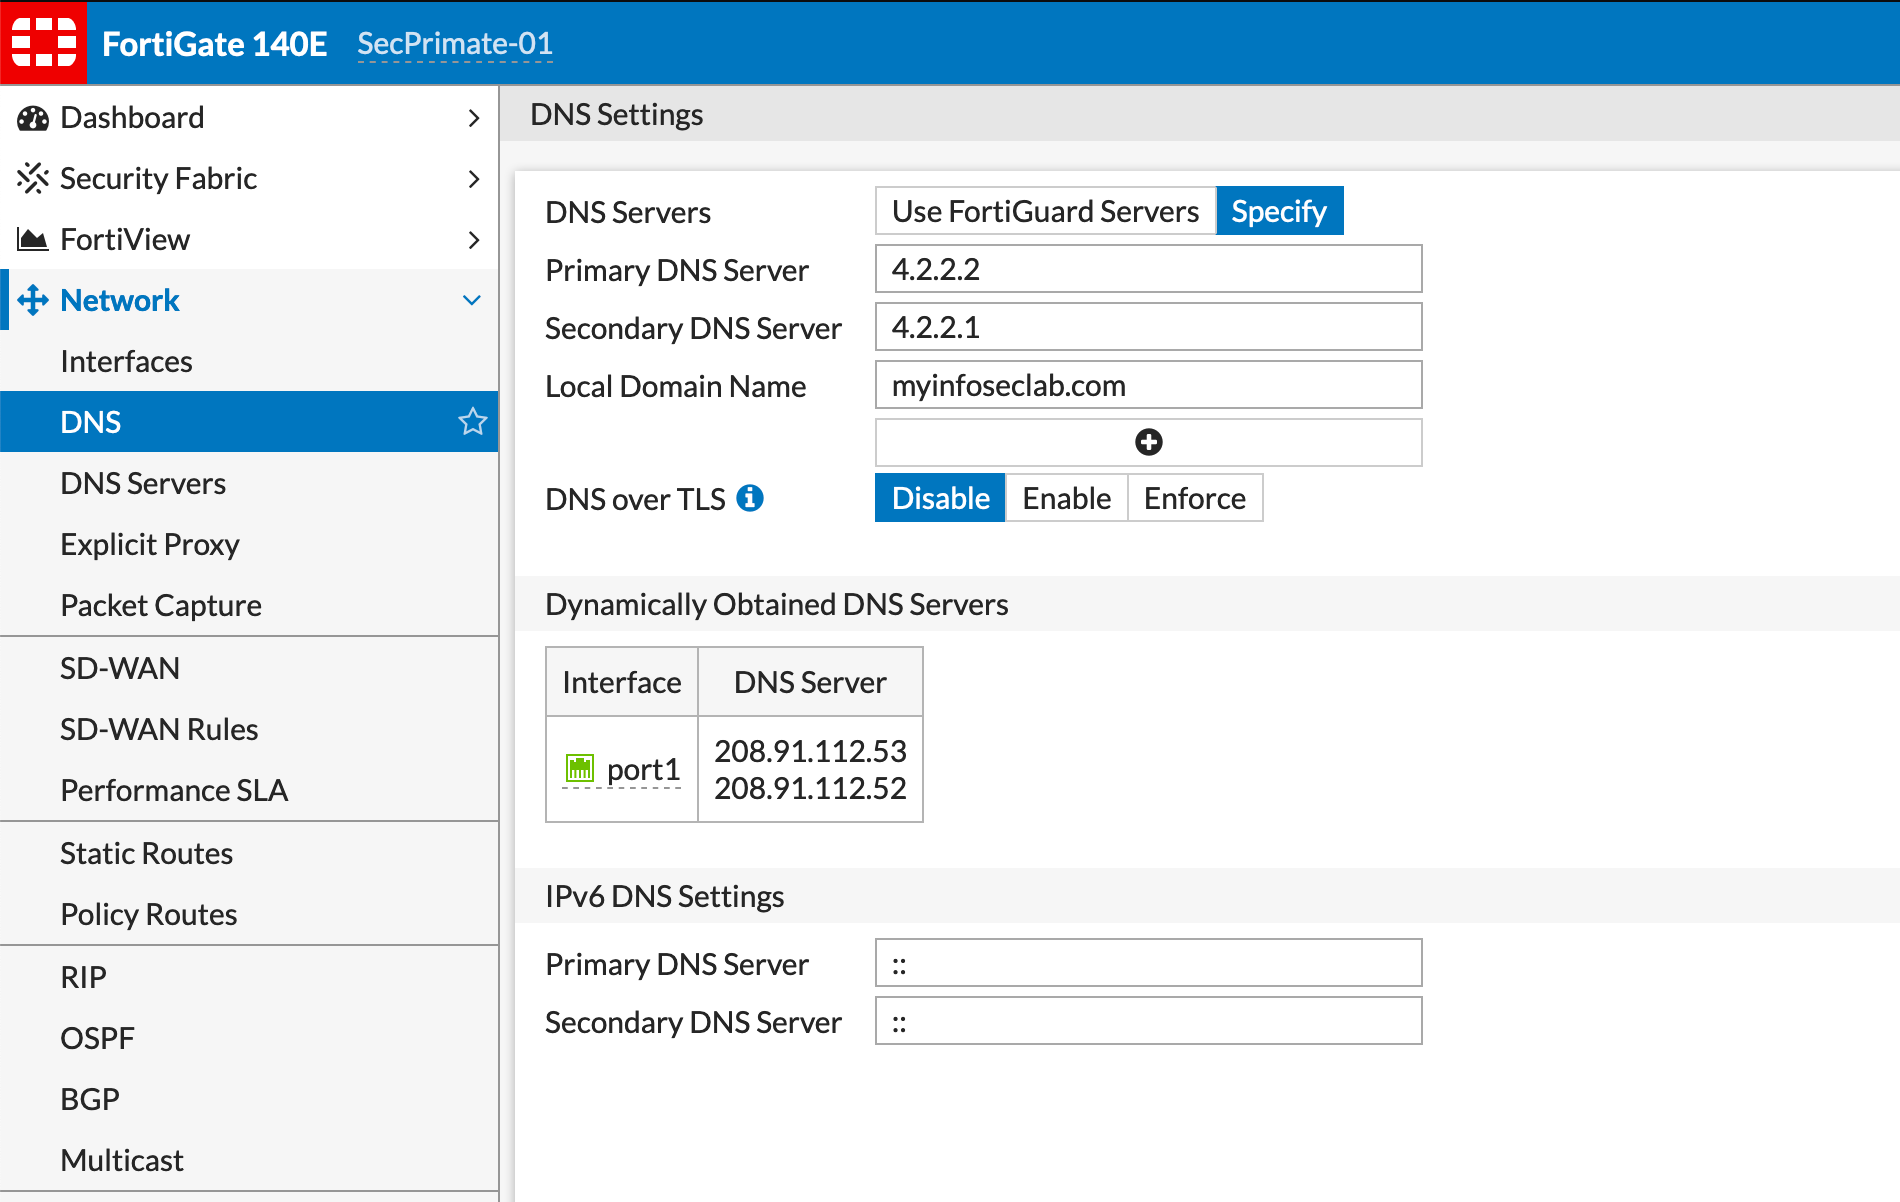
2019-11-19_20-20-14.png

Here we can see the DNS over TLS is disabled, which is the default.
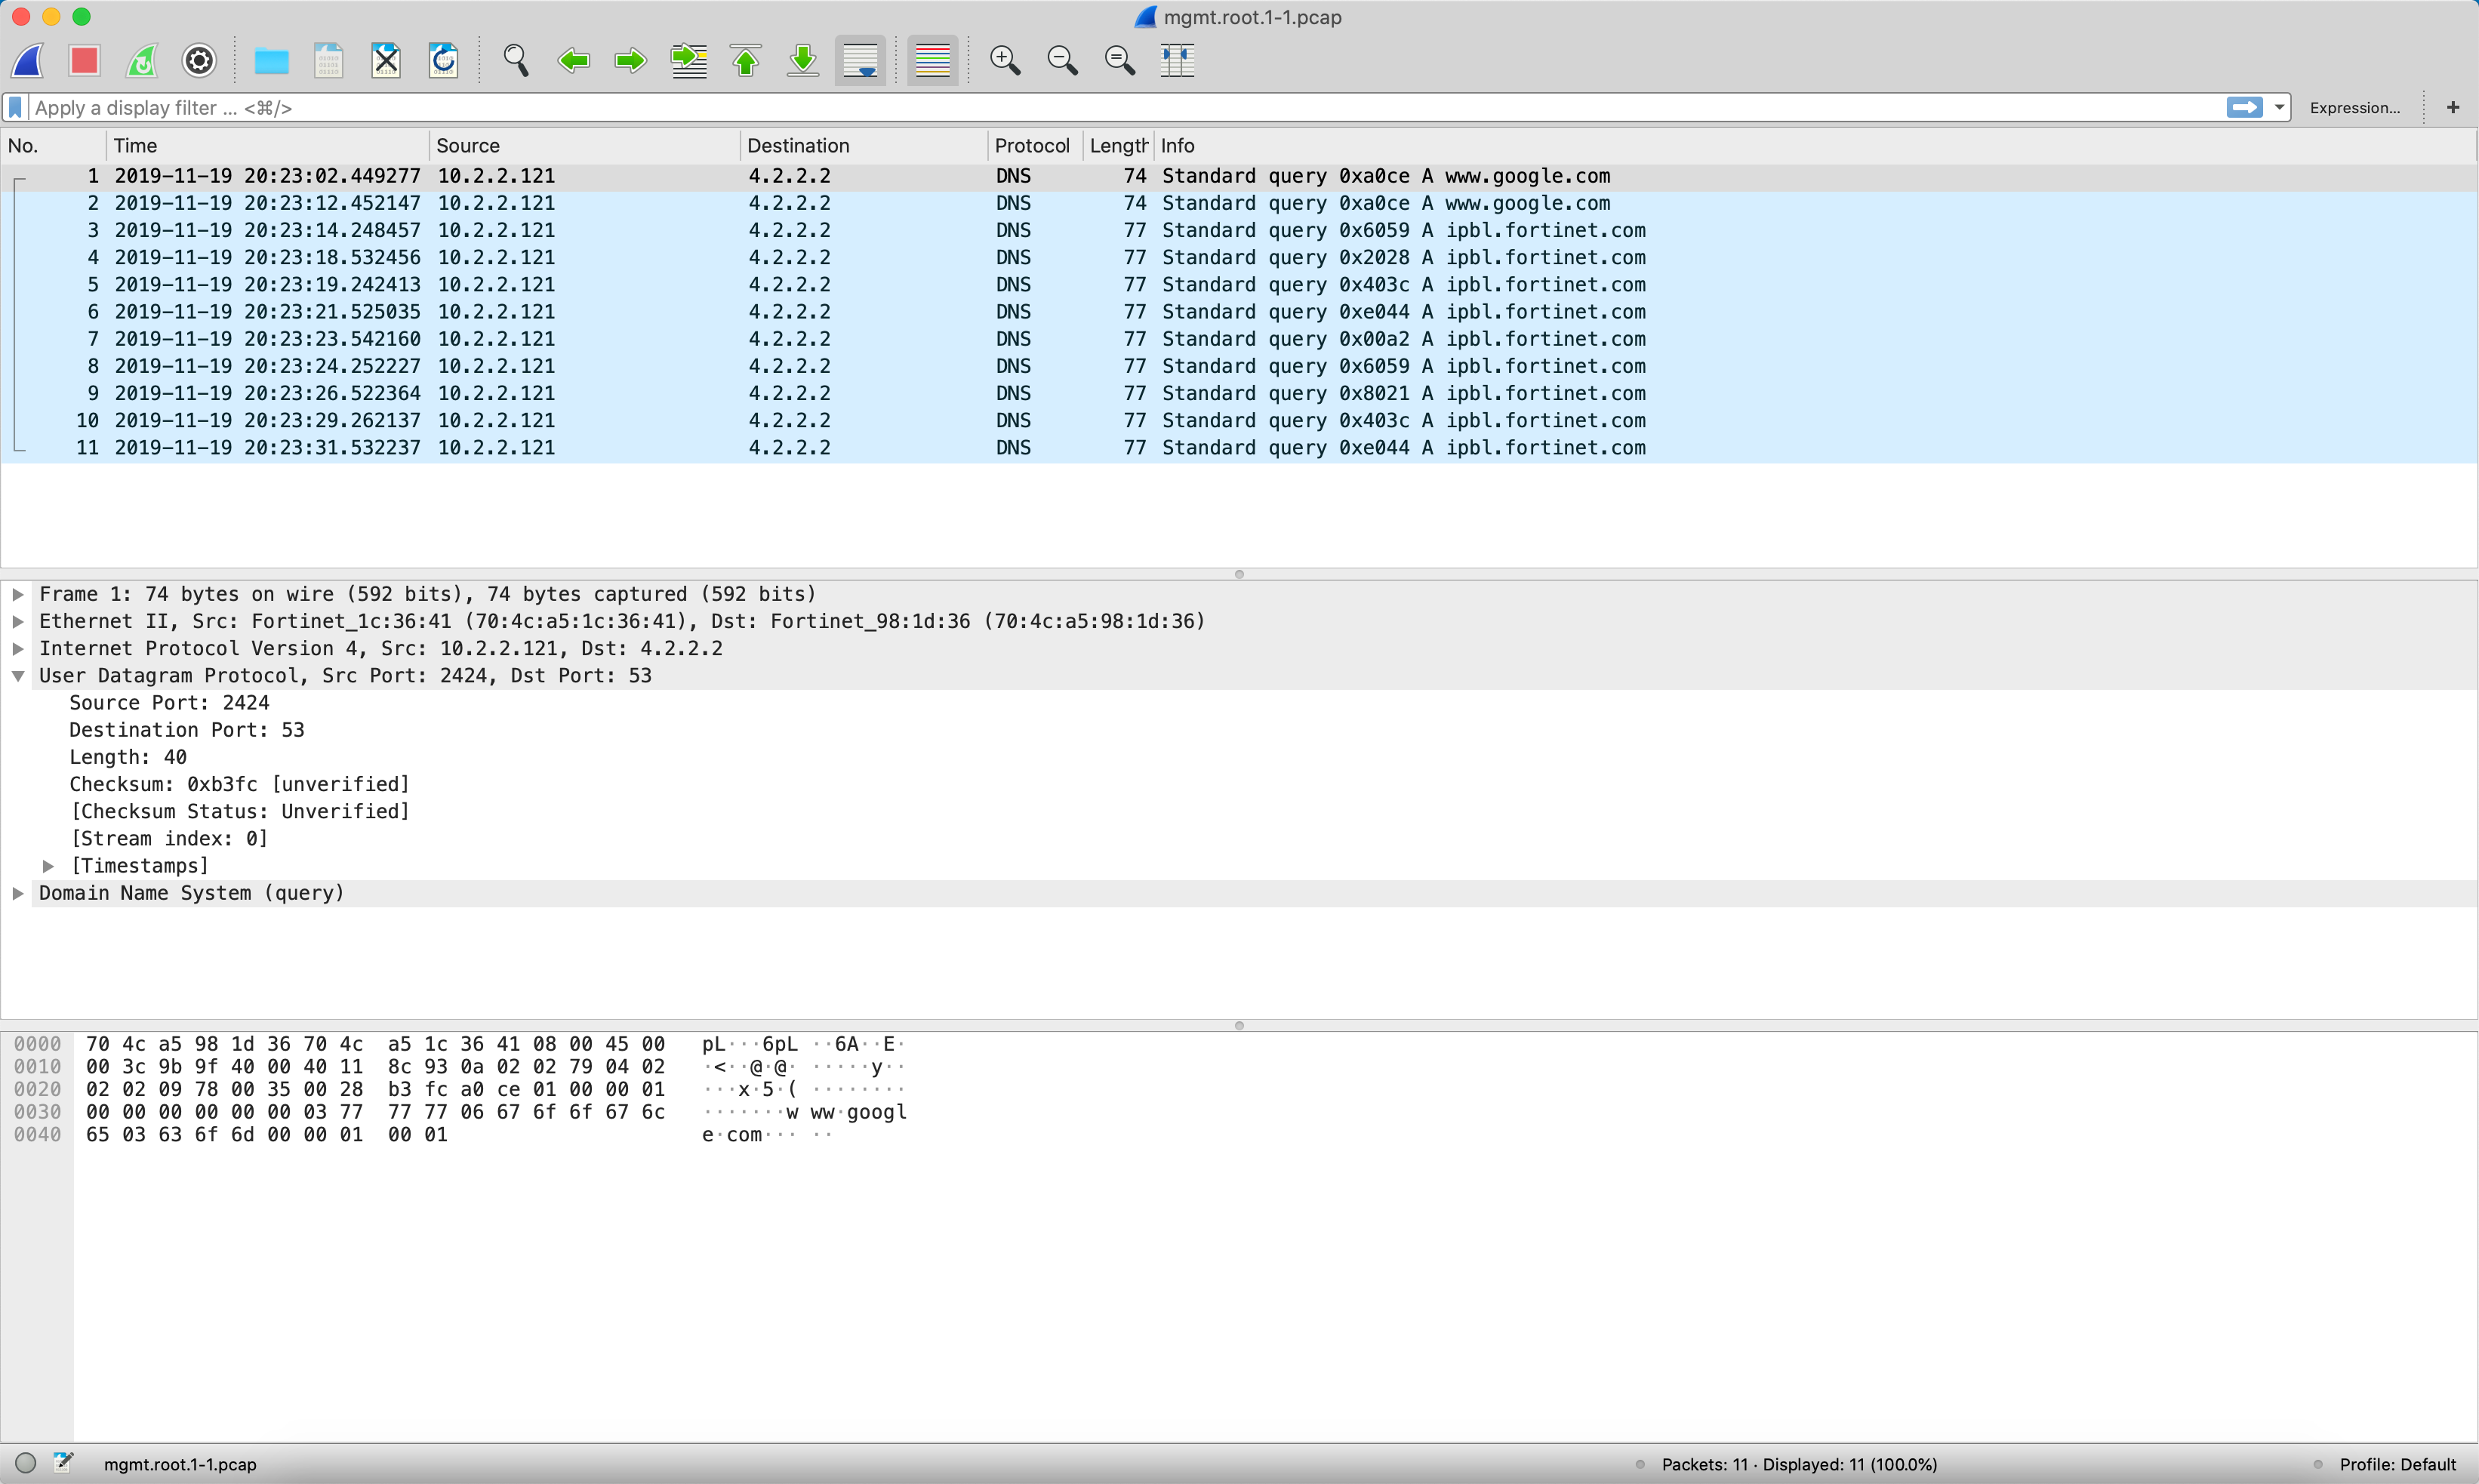
2019-11-19_20-24-06.png

Here we can see a packet capture showing a standard DNS query.  As you see this traffic is UDP 53.
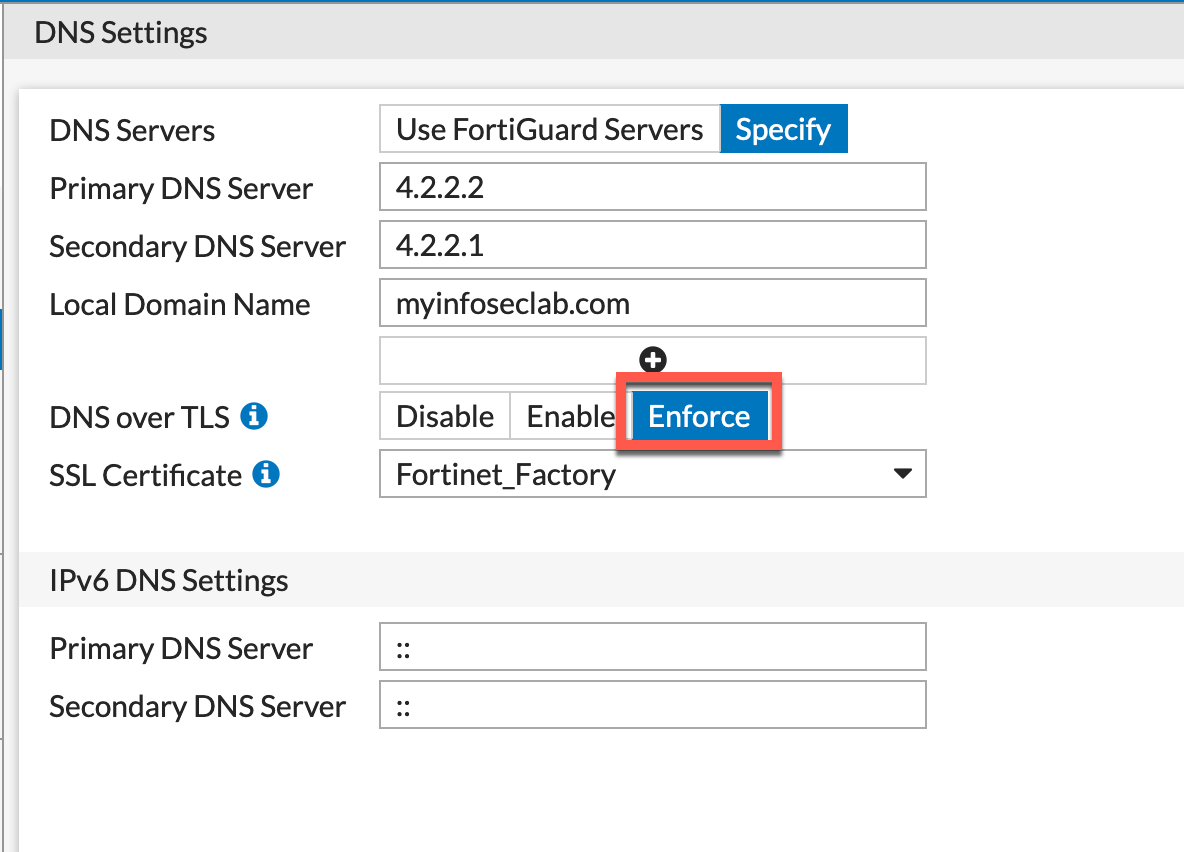
2019-11-19_23-14-14.png

In the screenshot above, we can see that this is set up in Enforce mode which is Strict mode.  You will need to choose the certificate you want to use from the drop down.
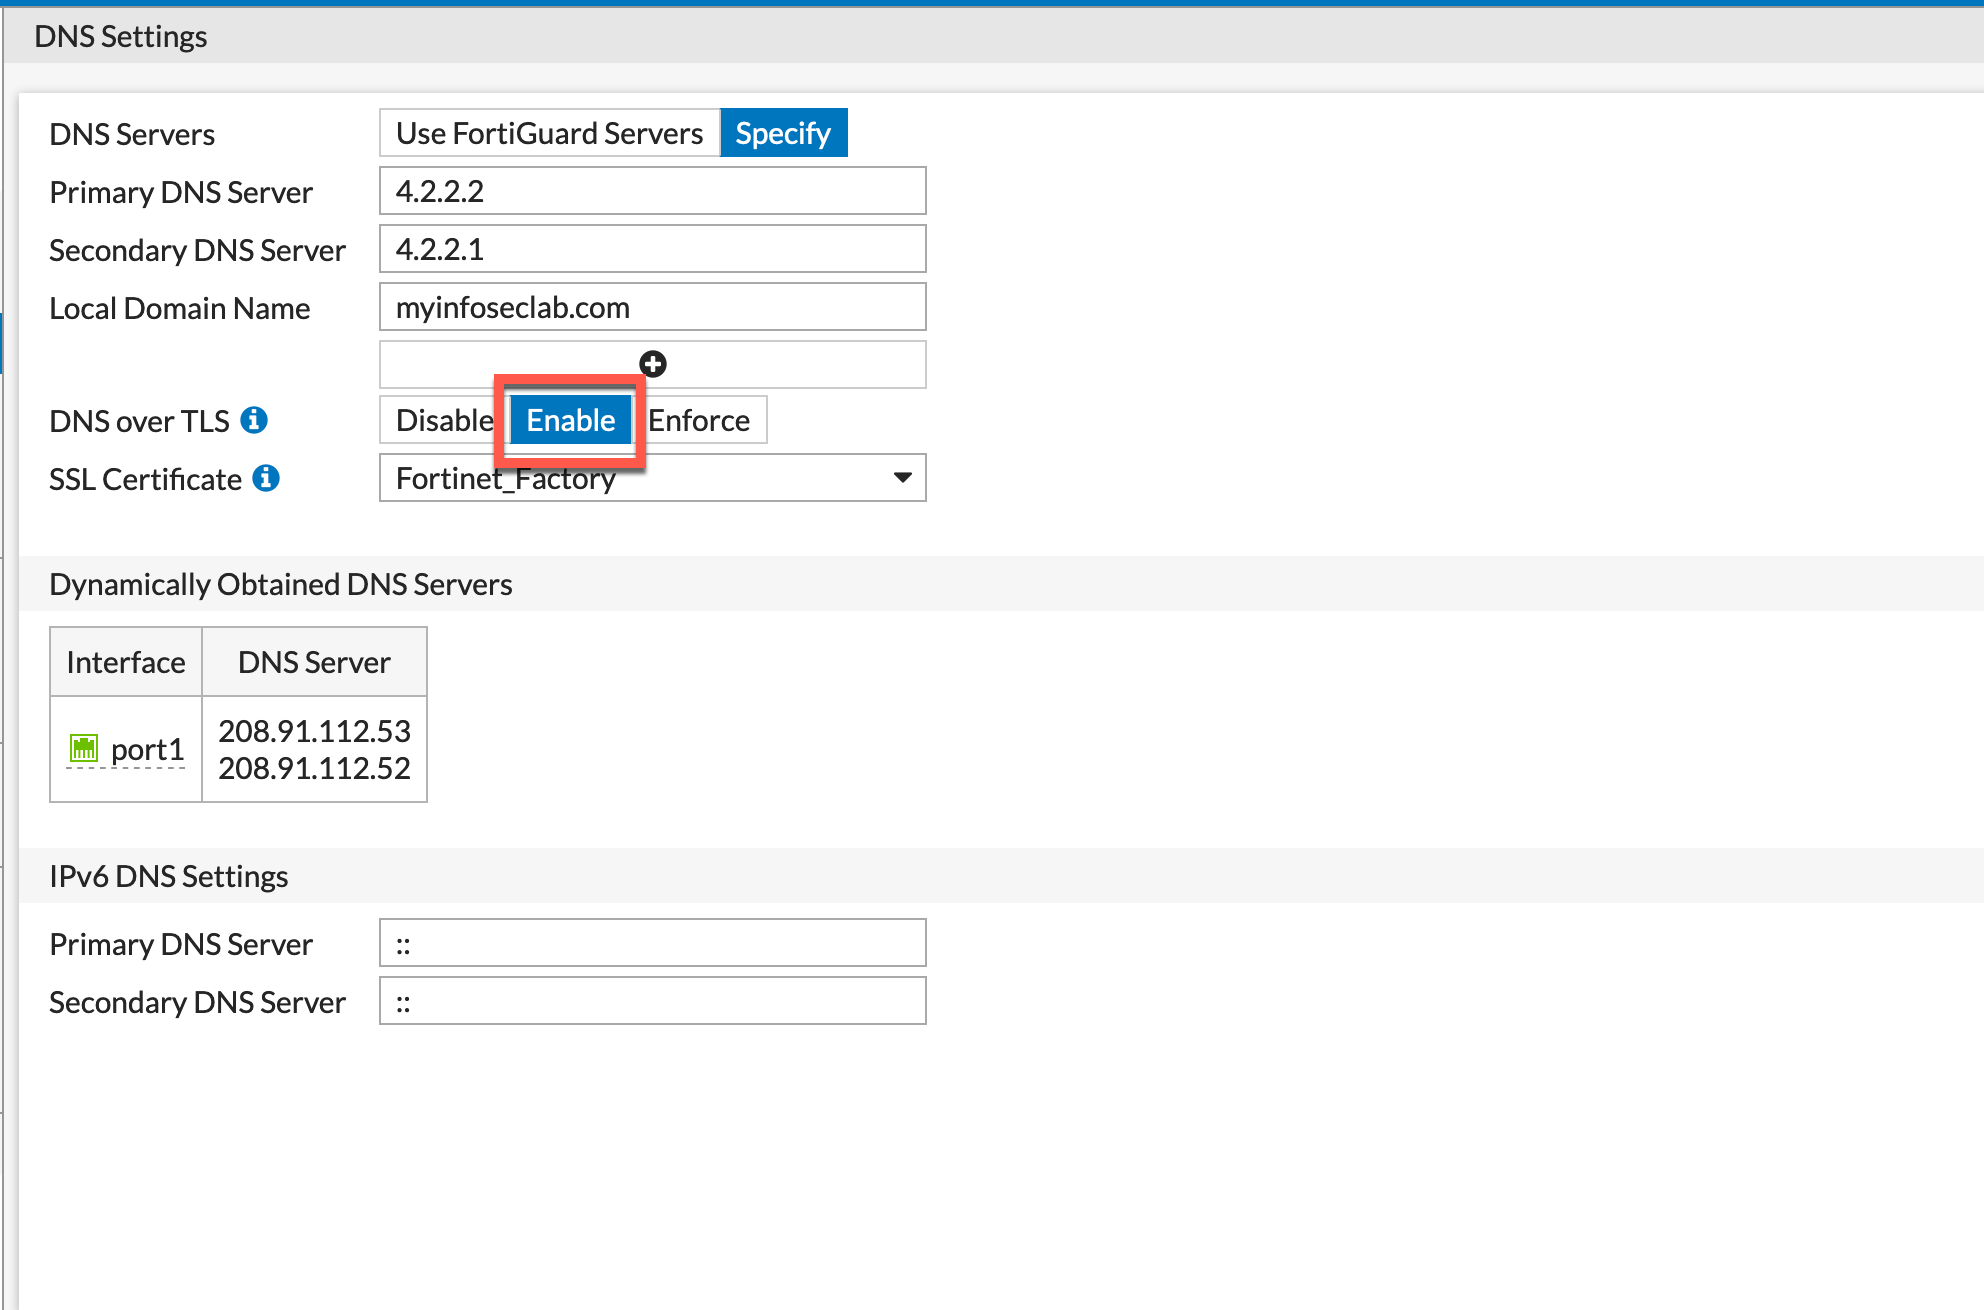
2019-11-19_20-24-54.png

With the Enable option here,  this is actually opportunistic mode.  In this mode, the client will attempt to make a TLS connection on port 853 and if it fails, it will fall back to the standard UDP 53.
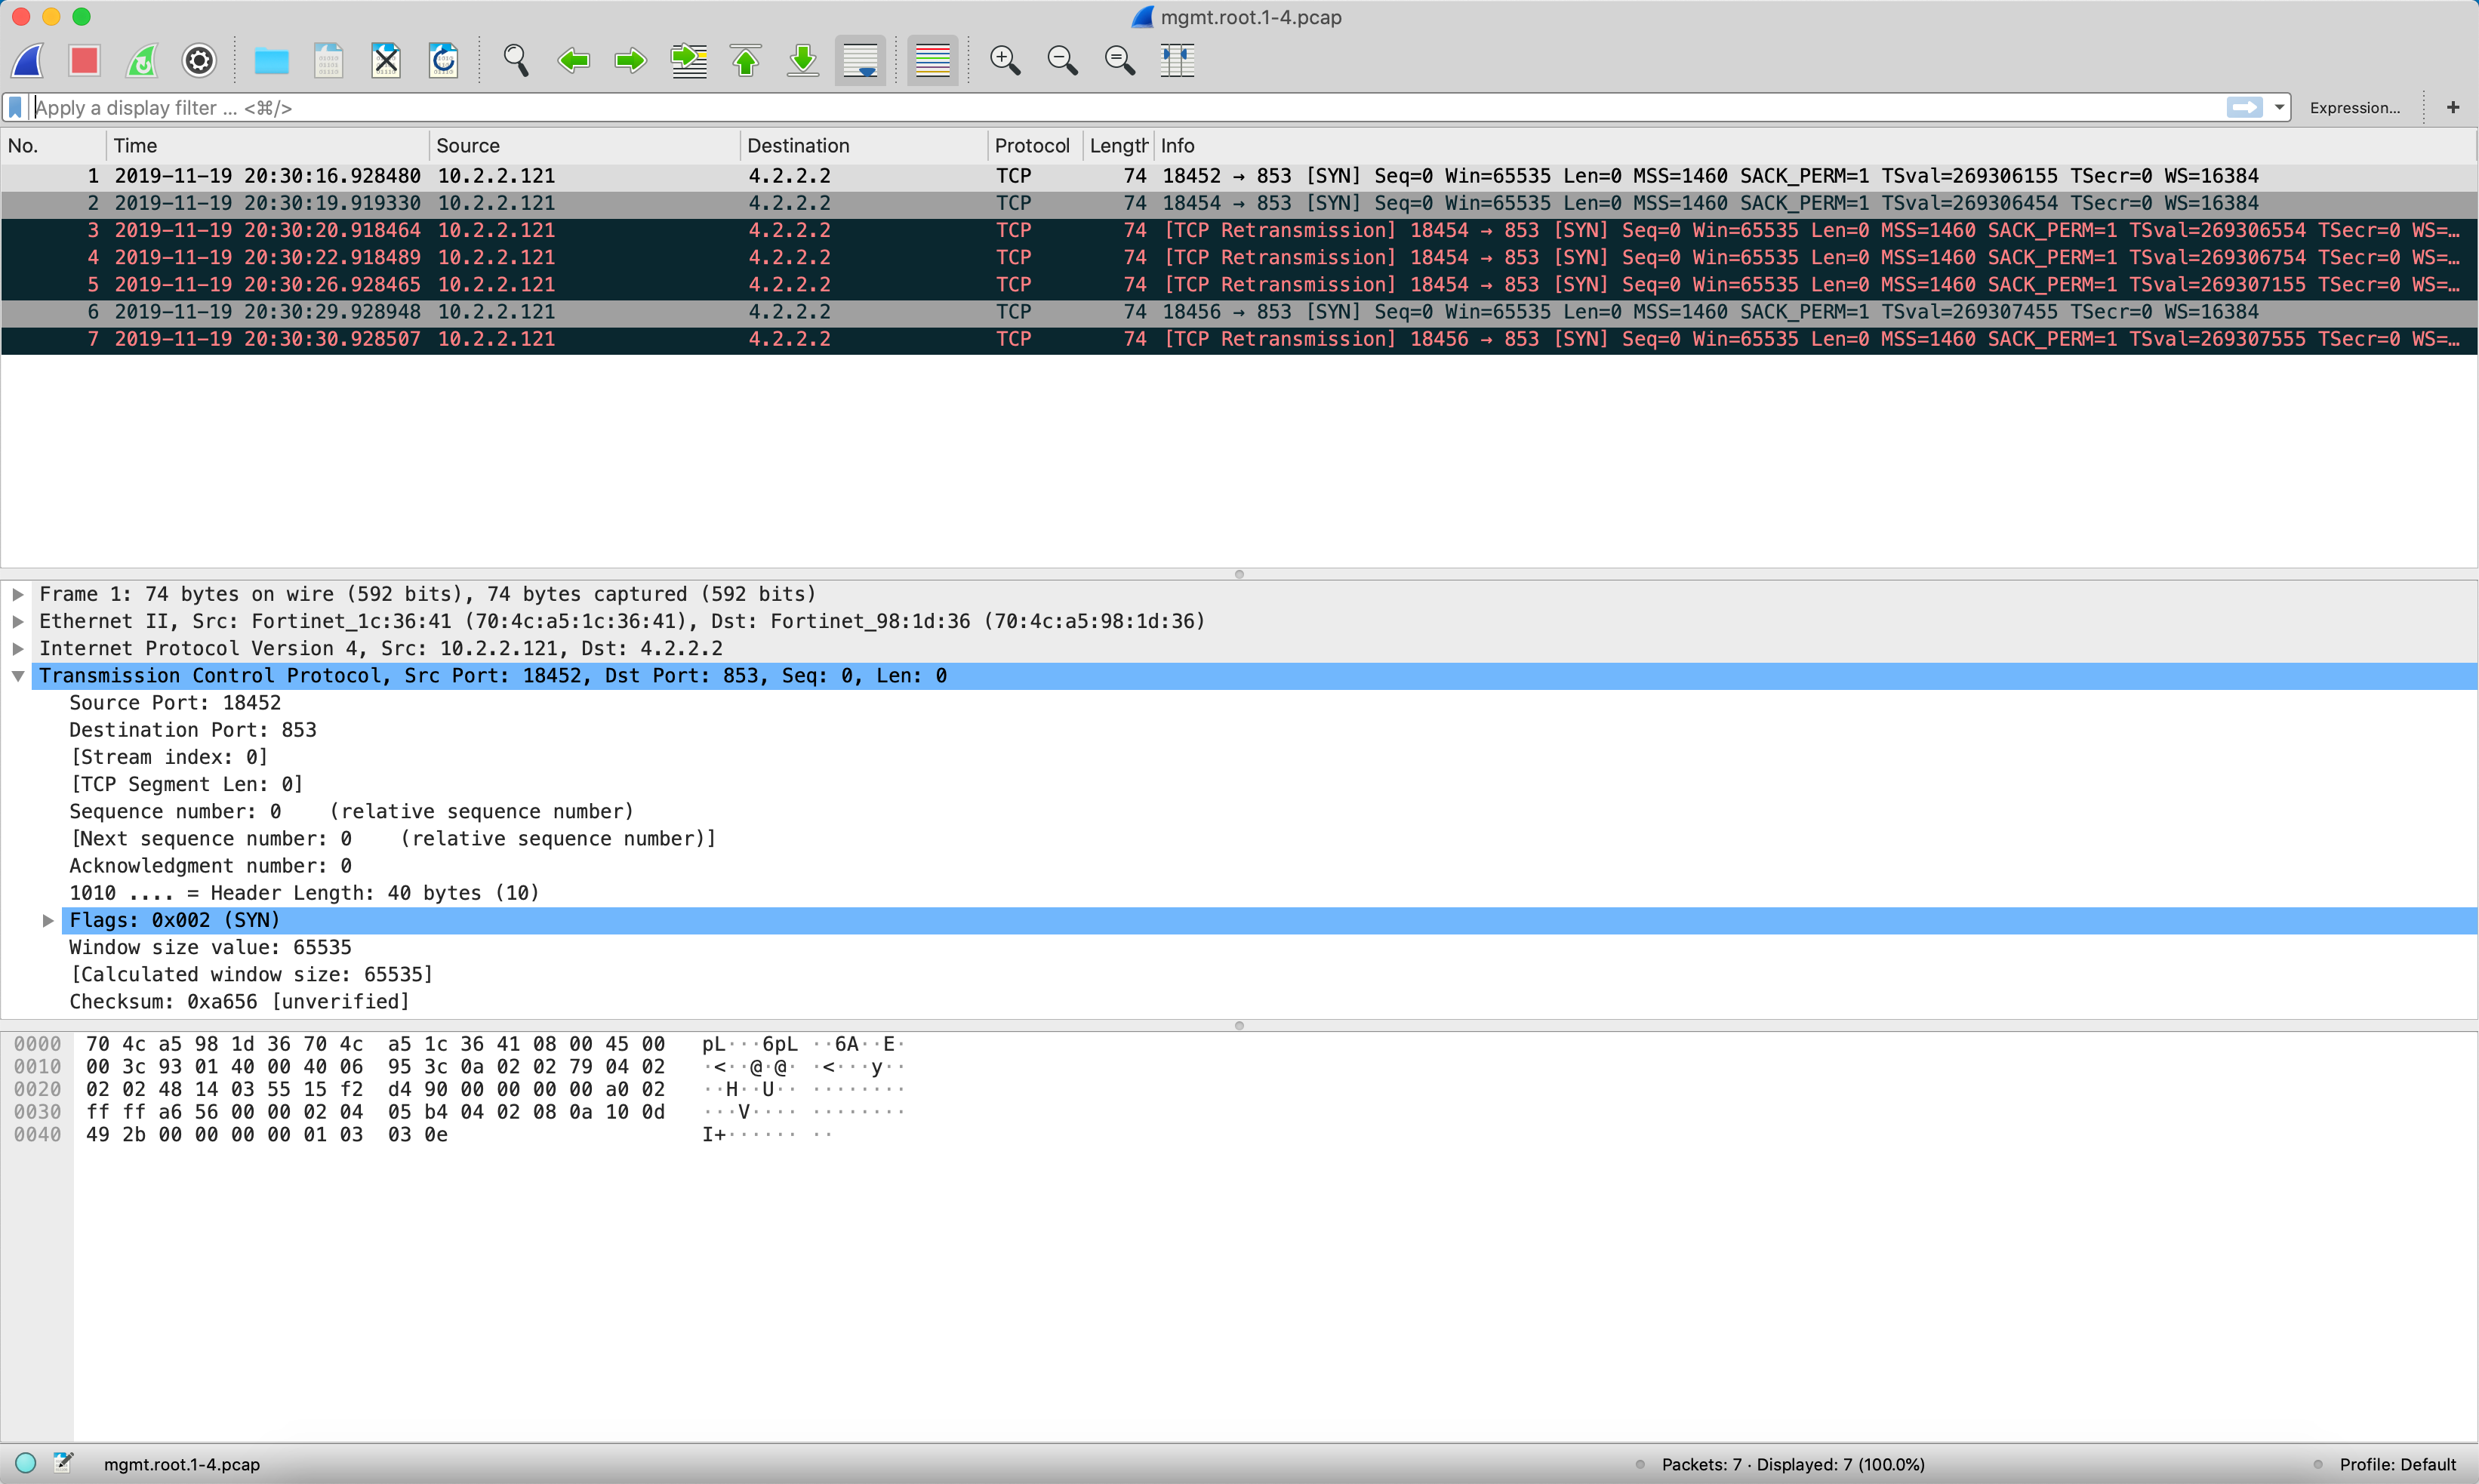
2019-11-19_20-30-50.png

Here you can see the packet capture after turning on DoT.  Notice it is using TCP and is using port 853.

DoH Blocking

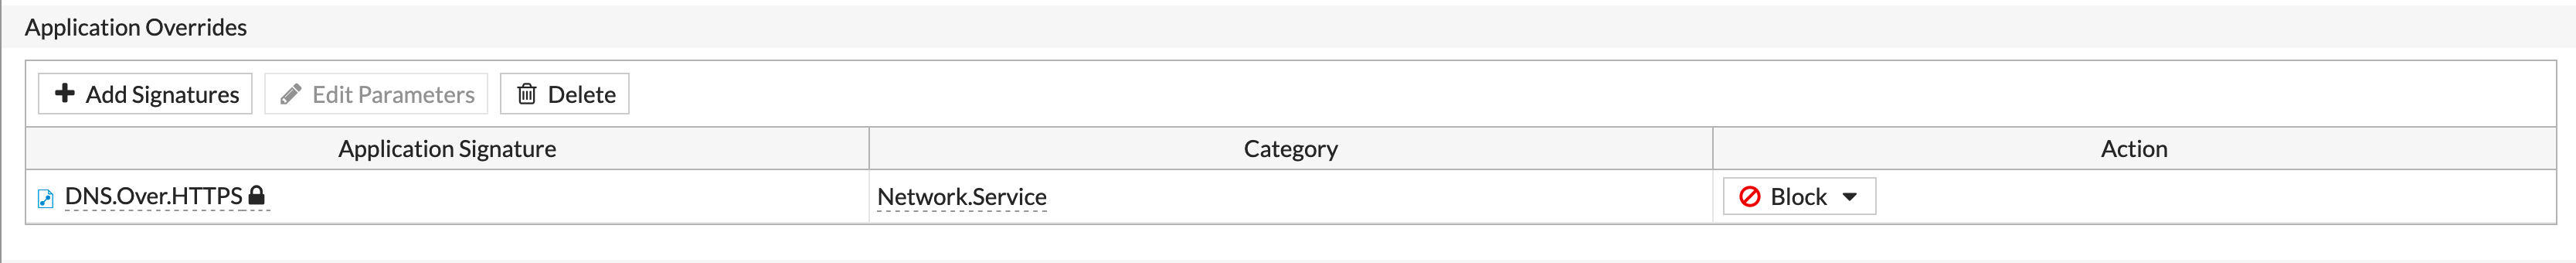
If you want to block DNS over HTTPS, Fortinet has a application signature for it.
2019-11-19_22-46-10.png

WHOIS Protocol: History, Limitations, and What Replaced It

WHOIS Protocol: History, Limitations, and What Replaced It

Learn how the WHOIS protocol grew from a 1982 ARPANET directory, why port 43 falls short today, and what replaced it for domain lookups.

Read More
RFC2136 Dynamic DNS on Ubuntu: Deploy BIND9 with TSIG-Secured Updates

RFC2136 Dynamic DNS on Ubuntu: Deploy BIND9 with TSIG-Secured Updates

Build an authoritative BIND9 server on Ubuntu that accepts RFC2136 dynamic DNS updates, signed with TSIG keys and scoped per client with update-policy, then...

Read More
FortiGate DDNS: `config system ddns` Actionable Configuration

FortiGate DDNS: `config system ddns` Actionable Configuration

Configure FortiGate config system ddns for FortiGuard, No-IP, and RFC 2136. Get working CLI syntax for dual WAN, IPv6, and upstream NAT scenarios.

Read More