The Fortigate 6300 Is a massive platform with so much power, it can be used in multiple deployment methods; from the edge to the network core and everywhere in-between. The archatecture of this box is a virtual chassis as it is not a “True” chassis (see above) but has 6 blades. Sometimes you have protocols that do not play nice being load-balanced across the 6 blades. Below, I will show you a quick work around.
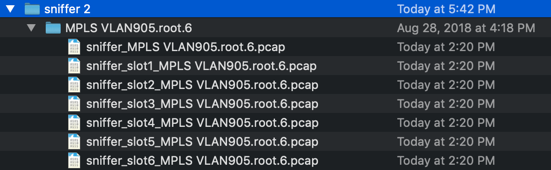
In the 6K, when you perform a packet capture from the GUI (Standard in all 6.0.2 +) you will get an output with 6 PCAPs; one per blade. This way you can see what blade the traffic is traversing.
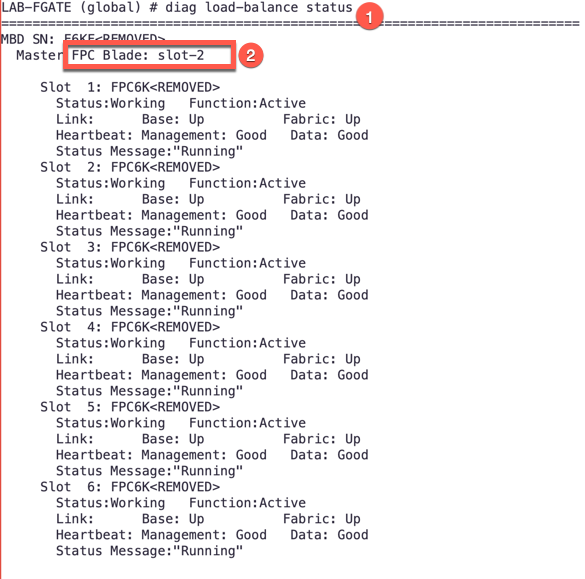
In the figure above, we can see the slot 2 is the master blade. You can determine this by typing the following command: ‘diag load-balance status’
If you connect to the 6300 via the console or SSH, you can access the section that controls ‘nailed blade connections’.
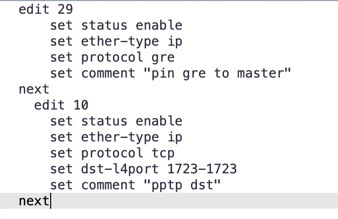
‘config load-balance flow-rule’
you can enter the ‘show’ command and see what has already been added. You can then make changes as needed in the typical Fortigate method.
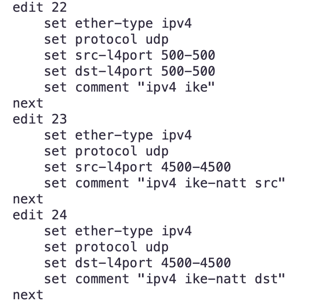
Here we can see that the IPv4 IKE and NAT-T (source and destination) are nailed to the master blade.
I had a customer that was running PPTP before the 6300 install. He still needed to maintain this environment until he cut everyone over to FortiClient. PPTP was breaking so we needed to add an entry to force it to remain on the main blade.
Hope this helps.